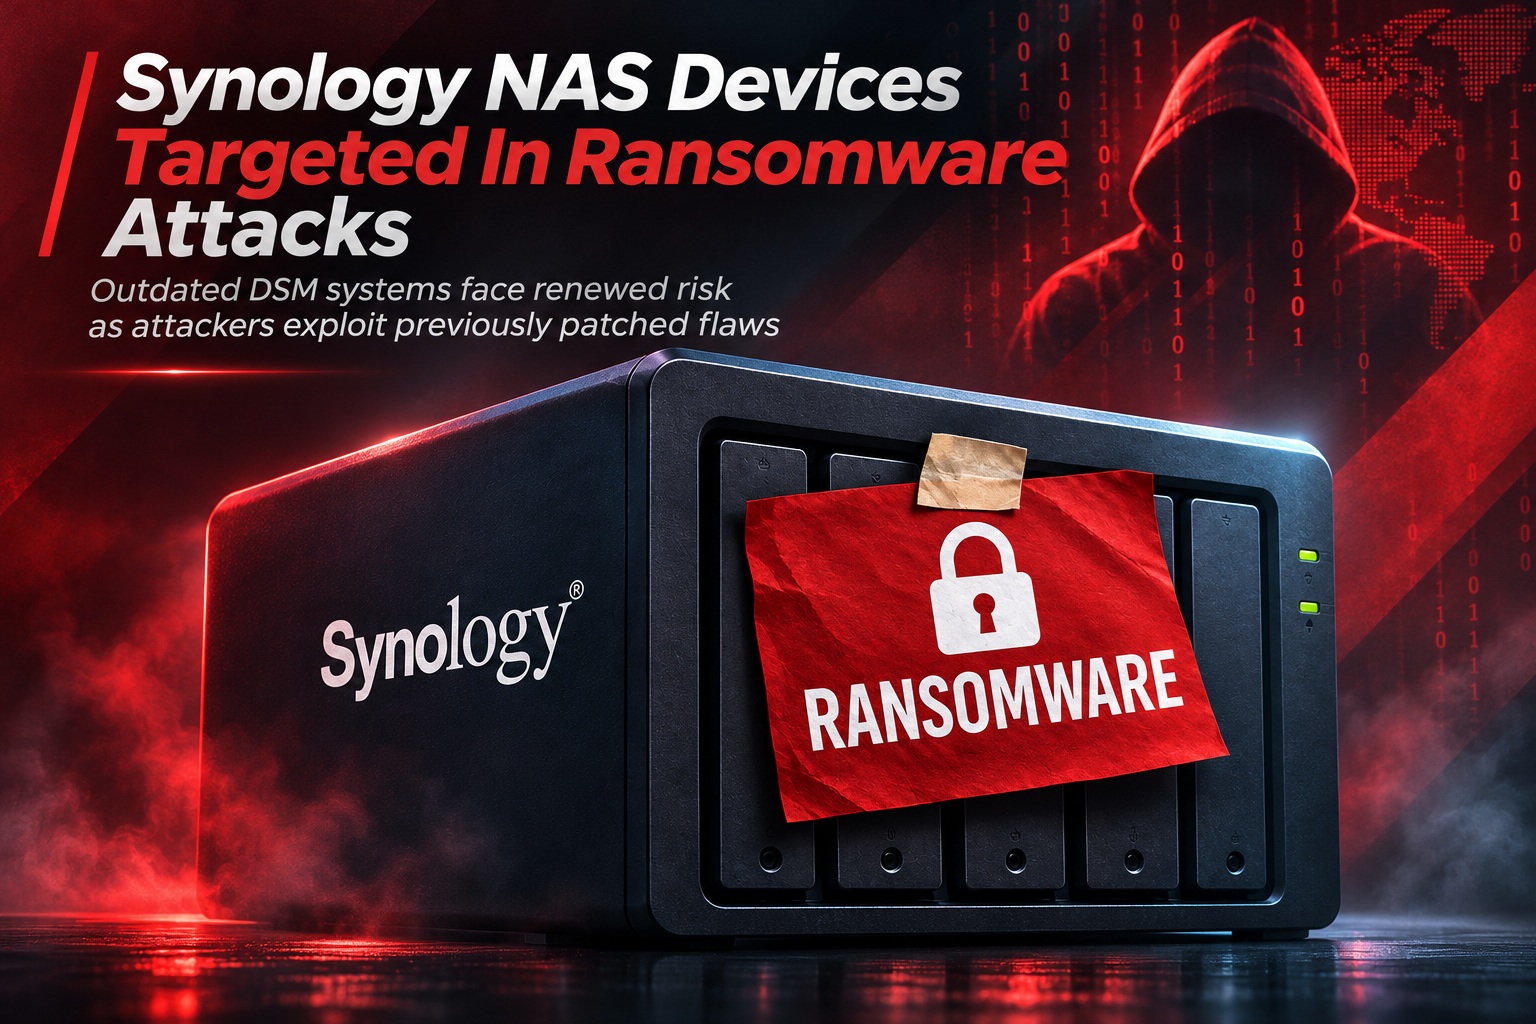
Synology is warning customers to update the DiskStation Manager software running on its Network Attached Storage devices after detecting ransomware attacks against systems using outdated DSM versions. According to the company, attackers are exploiting a vulnerability that Synology had already fixed in December 2024, with the goal of encrypting stored data and demanding ransom payments from victims. The attacks underline a familiar problem in cybersecurity: a vulnerability may be fixed by the vendor, but systems remain exposed as long as users delay installing the available update.
Synology Says Outdated DSM Versions Are Being Exploited
The Taiwanese storage vendor said it had observed threat actors actively targeting Synology NAS devices that had not yet been upgraded to patched DSM releases. The company did not publicly identify the exact vulnerability currently being abused, but it pointed users towards a security advisory originally published in November 2024. That advisory covered three separate DSM vulnerabilities, one of which carries a critical CVSS score of 9.8 and could potentially enable remote code execution. Synology is therefore urging customers to treat outdated DSM installations as a serious security risk rather than something that can safely remain unchanged simply because the NAS still appears to function normally.
CVE-2024-10441 Is The Most Severe Flaw In The Advisory
The most serious vulnerability listed in the November 2024 advisory is CVE-2024-10441, which carries a CVSS score of 9.8. The flaw involves improper encoding or escaping of output within DSM's system plugin daemon and could potentially allow remote code execution through unspecified attack vectors. Remote code execution is particularly dangerous because it can give an attacker the ability to run commands directly on the NAS without needing normal administrative access. If such a flaw is successfully exploited, the attacker may be able to install malware, modify files or launch ransomware directly from the compromised device.
CVE-2024-50629 Can Expose Files Remotely
Another vulnerability in the same advisory is CVE-2024-50629, which has a lower CVSS score of 5.3. This flaw affects the DSM webapi component and could allow a remote attacker to read a limited number of files through unspecified vectors. While the potential impact is narrower than full remote code execution, unauthorised file access can still expose sensitive configuration data, documents or other information stored on the system. In some attack chains, a lower-severity information disclosure flaw may also help attackers gather information needed to exploit other weaknesses more effectively.
CVE-2024-10445 Can Allow Limited File Writing
The third vulnerability from the 2024 advisory is CVE-2024-10445, which carries a CVSS score of 4.3. It affects DSM's update functionality and involves improper certificate validation, potentially allowing remote attackers to write a limited number of files to the device. On its own, this may not appear as severe as remote code execution, but unauthorised file writing can still be useful to an attacker attempting to establish persistence or modify system behaviour. As with many vulnerabilities, the risk becomes more serious when several weaknesses can be combined together.
Several DSM Versions Need Specific Security Updates
Synology has already released fixed DSM versions across several supported branches, meaning affected users should verify exactly which release they are running. Devices on DSM 7.2.2 should be upgraded to 7.2.2-72806-1 or later, while systems on DSM 7.2.1 should move to 7.2.1-69057-6 or above. Those still using DSM 7.2 need at least 7.2-64570-4, while DSM 7.1 users should update to 7.1.1-42962-7 or later. Older DSM 6.2 systems require 6.2.4-25556-8 or above to receive the relevant fixes.
C3RB3R Ransomware Is Reportedly Hitting Synology Devices
The warning comes amid reports from Synology users that their NAS devices have been compromised by C3RB3R ransomware. Victims have reported files being renamed with the ".L0CK3D" extension, a clear indication that the malware has encrypted the data and rendered it inaccessible without whatever decryption process the attackers demand. A ransom note named "read-me3.txt" is also reportedly placed inside affected directories. This behaviour is consistent with ransomware operations designed to make recovery difficult while directing victims towards the attackers' payment instructions.
C3RB3R Has A History Of Targeting NAS Systems
Chinese security company Qihoo 360 Internet Security Center described C3RB3R as a ransomware operation with a long history of targeting NAS devices. Network Attached Storage systems can be particularly attractive targets because they often hold large amounts of centralised data, including backups, business documents, photographs and shared files. For small businesses and home users, a single NAS may contain years of important information, making encryption extremely disruptive. Attackers know this and can use the importance of the stored data as leverage when demanding ransom payments.
The Ransomware Carefully Avoids Breaking The NAS
Once active on a compromised device, C3RB3R reportedly scans stored files and begins encryption while deliberately skipping certain directories and file extensions. The malware avoids 27 directories and ignores files using extensions such as BAT, DLL, EXE, LNK, MOD, MSI and SYS. This behaviour appears intended to prevent the ransomware from damaging system components needed to keep the NAS running during the attack. By avoiding critical files, the malware can continue encrypting user data without crashing the device before the operation is complete.
Encrypted Files Receive The .L0CK3D Extension
Files successfully encrypted by the ransomware are renamed with the .L0CK3D extension, making it immediately obvious which data has been affected. The attackers then place a ransom note called read-me3.txt inside encrypted directories, presumably containing instructions for victims to contact or pay them. This type of behaviour is common among ransomware groups because it ensures the payment instructions remain visible even when large portions of the victim's storage have become inaccessible. The presence of the renamed files and ransom note usually means the attack has already progressed well beyond the initial compromise stage.
Newer DSM Vulnerabilities Were Also Exploited In September 2026
C3RB3R has reportedly also exploited more recent DSM vulnerabilities that Synology patched in September 2026. These vulnerabilities are tracked as CVE-2026-13684 and CVE-2026-13639, and both carry critical CVSS scores of 9.8. This shows that the ransomware operators are not relying on one old exploit alone but are willing to adopt newly disclosed weaknesses when vulnerable NAS devices remain available. For administrators, this means patching one historical vulnerability is not enough if the system continues falling behind on later DSM releases.
CVE-2026-13684 Can Read Or Write Arbitrary Files
CVE-2026-13684 involves improper encoding or escaping of output in Synology's SCGI implementation. A remote attacker could potentially use the vulnerability to read or write arbitrary files and conduct denial-of-service attacks against affected systems. The ability to write arbitrary files is particularly serious because it may allow attackers to place malicious content or ransomware components directly onto the NAS. Combined with other weaknesses, this type of access can become part of a full compromise chain.
CVE-2026-13639 Targets DSM Login Logic
The second 2026 vulnerability, CVE-2026-13639, involves insufficient entropy in DSM's login logic. It can also allow remote attackers to read or write arbitrary files and cause denial-of-service conditions. Weaknesses in authentication or login-related logic are especially concerning because they may allow attackers to gain access without first compromising a legitimate administrator account. Both 2026 flaws were already patched by Synology, reinforcing the company's current message that users need to keep DSM continuously updated rather than applying security fixes only occasionally.
NAS Devices Have Been Ransomware Targets For Years
This is not the first time attackers have focused specifically on NAS products. In 2019, QNAP devices were targeted by QNAPCrypt, also known as eCh0raix, a ransomware family designed specifically to compromise and encrypt data stored on NAS appliances. The popularity of such attacks reflects how valuable these systems can be to users and businesses. When centralised storage becomes unavailable, entire teams may lose access to shared documents and backups at the same time.
Synology Faced Brute-Force Ransomware Attacks In 2021
Synology itself warned users in August 2021 about attacks involving a malware family called StealthWorker. Those attacks relied heavily on brute-force techniques, with already compromised devices attempting to guess common administrative credentials on other Linux-based systems, including Synology NAS appliances. Once attackers successfully gained access, they could install malicious payloads including ransomware and then use the newly compromised system to attack additional devices. The incident demonstrated how weak administrator passwords can become just as dangerous as software vulnerabilities.
Common Administrative Credentials Remain A Major Risk
Brute-force attacks continue to work because many devices still use predictable administrator usernames and passwords. Attackers can automate thousands of login attempts using common password lists until they discover a combination that works. A NAS exposed directly to the internet becomes much more vulnerable when remote administration is available and credentials are weak or reused elsewhere. Strong unique passwords and multi-factor authentication therefore remain important even when all known software vulnerabilities have already been patched.
eCh0raix Also Targeted Both QNAP And Synology Devices
Around the same period in 2021, security researchers documented another eCh0raix variant targeting both QNAP and Synology NAS devices. Attackers reportedly used a combination of software vulnerabilities and brute-force login attempts involving commonly used administrative credentials. This mixed approach illustrates how ransomware groups rarely depend on one technique exclusively. If a vulnerability fails, stolen or guessed credentials may provide another route into the same device.
Internet-Exposed NAS Devices Face Greater Risk
A NAS is much easier to attack when its management services are accessible directly from the public internet. Remote access may be convenient, but it also exposes login pages and other services to automated scanners continuously searching for vulnerable devices. Attackers can identify product types, software versions and open ports without knowing anything about the organisation beforehand. Reducing unnecessary exposure can therefore significantly shrink the number of attack opportunities available.
Remote Access Should Be Restricted Wherever Possible
Users who do not genuinely need direct internet access to their NAS should consider restricting external management interfaces and services. Remote administration can instead be placed behind a VPN or another controlled access mechanism rather than allowing every internet address to reach DSM directly. Firewall rules can also restrict access to known networks or trusted addresses. These controls do not replace patching, but they can prevent many automated attacks from reaching vulnerable services in the first place.
Automatic DSM Updates Can Reduce Exposure
Synology strongly recommends enabling automatic updates so security patches are applied promptly when new DSM releases become available. Many NAS compromises occur not because fixes do not exist, but because the affected system remains several versions behind long after a vulnerability has been publicly disclosed. Attackers benefit from this delay because published advisories and patches can help them understand where the original weakness exists. Keeping DSM updated reduces the amount of time between Synology releasing a fix and the device actually becoming protected.
Automatic Updates Are Particularly Useful For Home Users
Home users may not regularly monitor security advisories or check DSM release notes, making automatic updates particularly valuable. A NAS may continue operating reliably for years, encouraging owners to avoid changing anything as long as files remain accessible. Unfortunately, a device that appears perfectly healthy can still contain remotely exploitable vulnerabilities. Automatic security updates help protect users who may not otherwise know that urgent patches are available.
Businesses Should Still Test Important Updates
Organisations running business-critical Synology systems may prefer controlled patching rather than installing every release immediately without testing. In those environments, updates should still be deployed quickly but may first pass through validation on non-production devices or during planned maintenance windows. The important point is that testing should not become an excuse for leaving critical vulnerabilities unpatched indefinitely. A defined emergency patching process helps balance stability with security.
Backups Need To Be Protected From The NAS Itself
Ransomware targeting a NAS becomes especially dangerous when the device also stores the organisation's only backup. If attackers compromise the system and encrypt everything accessible from it, the supposed backup may disappear at exactly the moment it is needed. Important data should therefore exist in multiple locations, with at least one backup isolated from the primary NAS. Offline or immutable backups can provide another recovery option when the main storage system is compromised.
A RAID Array Is Not A Ransomware Backup
NAS users sometimes assume RAID protects them from ransomware because data is stored across multiple drives. RAID provides resilience against certain hardware failures, but it does nothing when ransomware intentionally encrypts files at the logical storage level. Every drive in the array simply stores the encrypted version of the data. Proper backups need independent copies that the compromised NAS cannot freely modify.
Snapshots Can Help But Need Proper Protection
Storage snapshots can provide useful protection against accidental deletion or ransomware, particularly when they are immutable or protected from ordinary administrator accounts. However, attackers with sufficient privileges may attempt to delete or encrypt snapshots before targeting the main files. Organisations should therefore understand how snapshots are protected and whether a compromised DSM administrator account can remove them. Snapshot retention should complement external backups rather than replace them entirely.
Unusual File Extensions Can Be An Early Warning Sign
The sudden appearance of unfamiliar extensions such as .L0CK3D should immediately trigger investigation. Users may first notice that ordinary documents no longer open or that filenames have changed unexpectedly across multiple folders. At that point, disconnecting the affected NAS from the network may help prevent further spread or communication with attacker infrastructure, although the exact incident-response steps should depend on the environment. The sooner the attack is identified, the greater the chance of limiting additional damage.
Ransom Notes Should Not Be Treated As Normal Files
A ransom note appearing across several directories is another obvious sign that the device has been compromised. Administrators should preserve evidence rather than immediately deleting everything or reinstalling the system because logs and malicious files may help determine how the attacker gained access. Understanding the initial compromise is important before bringing restored systems back online. Otherwise, a newly rebuilt NAS could simply be attacked again through the same unpatched vulnerability or exposed service.
Do Not Assume Paying Guarantees Recovery
Ransomware operators frequently promise decryption after receiving payment, but victims have no guarantee that the provided tool will work or that the attackers will honour the agreement. Poorly written ransomware may damage files permanently, while criminals can simply disappear after payment. Paying can also encourage future attacks by demonstrating that the operation is profitable. Reliable backups remain the safest recovery strategy because they reduce dependence on the attacker's cooperation.
Check The DSM Version Immediately
Synology users should confirm which DSM version their NAS is currently running rather than assuming automatic updates have already handled everything. Devices that were manually configured to delay updates, remain offline for long periods or run older supported branches may still be vulnerable. The version number should be compared against the minimum fixed releases published by Synology. If the installed build is older, the device should be updated as soon as practical.
Older DSM Branches Still Need The Correct Build
Running DSM 6.2 or an older 7.x branch does not automatically mean the device is protected or unsupported. Synology provided specific fixed builds across several maintained branches, including 6.2, 7.1, 7.2 and 7.2.1. Administrators therefore need to check the full build number rather than only the major DSM version. A system can appear to be on the correct release family while still missing the security update that actually closes the vulnerability.
Security Updates Should Be Part Of NAS Maintenance
A NAS should not be treated as a household appliance that can simply remain untouched for years once installed. It is a network-connected computer running services, applications and an operating system that all require security maintenance. DSM updates, package updates, password reviews and backup checks should therefore be part of regular administration. The more important the stored data becomes, the more important that maintenance becomes as well.
Unused Services Should Be Disabled
Every service running on a NAS creates another potential attack surface. File sharing protocols, web services, remote access functions and third-party packages should be enabled only when they are actually required. Disabling unused functionality reduces the number of components attackers can target and simplifies the overall security posture. This principle is particularly valuable for internet-connected NAS devices that may otherwise expose several unnecessary services.
Multi-Factor Authentication Should Be Enabled
DSM supports stronger authentication options that can reduce the impact of stolen or guessed passwords. Multi-factor authentication requires an attacker to obtain more than just the password before successfully logging into the administrative interface. While MFA would not necessarily prevent exploitation of an unauthenticated software vulnerability, it remains extremely effective against brute-force and credential-based attacks. Given Synology's history of NAS attacks involving guessed administrator credentials, enabling MFA is a sensible additional defence.
Default Administrator Accounts Should Be Reviewed
Attackers frequently target usernames such as "admin" because they are predictable and commonly enabled. Synology users should review whether default administrative accounts remain active and disable them when they are no longer required. Creating uniquely named administrator accounts increases the amount of information an attacker needs before attempting credential attacks. Account permissions should also be limited so ordinary users do not receive administrative capabilities unnecessarily.
Monitoring Can Help Detect Suspicious Access
DSM logs should be reviewed for unusual login attempts, unexpected IP addresses or configuration changes. Repeated failed logins from unfamiliar locations may indicate automated brute-force activity, while successful logins at unusual times can signal account compromise. Security notifications can help administrators respond faster rather than discovering the problem only after files have been encrypted. Monitoring is especially important for devices that remain reachable from outside the local network.
Ransomware Keeps Returning To NAS Devices For A Reason
NAS devices combine several qualities attractive to ransomware operators: large amounts of valuable data, long operating lifetimes and owners who may not patch frequently. They are often always powered on and may expose remote services for convenience. Small businesses may also depend heavily on them without having dedicated security staff monitoring the systems. This combination makes poorly maintained NAS infrastructure an appealing target for automated ransomware campaigns.
Final Thoughts
Synology's warning is another reminder that patched vulnerabilities remain dangerous when users do not install the patches. The company has observed ransomware attacks targeting NAS devices running outdated DSM versions, with attackers reportedly deploying C3RB3R ransomware to encrypt files, append the .L0CK3D extension and leave ransom notes throughout compromised storage.
Synology has not publicly confirmed which specific 2024 vulnerability is currently being exploited, but the advisory it referenced includes CVE-2024-10441, a critical 9.8-rated flaw capable of remote code execution, alongside two additional file-access vulnerabilities. C3RB3R has also reportedly exploited newer 2026 DSM vulnerabilities, demonstrating that the ransomware operators continue adapting their techniques as new weaknesses become available.
Users should immediately verify their DSM version, install the latest available security updates and enable automatic updates where appropriate. Remote administration should be restricted wherever possible, multi-factor authentication should be enabled and unnecessary network services should be disabled.
Most importantly, NAS owners should maintain independent backups that cannot be encrypted alongside the primary storage system. A Synology NAS can provide excellent centralised storage, but once it becomes the only place where important data exists, a ransomware attack can turn convenience into a single point of failure.






Comments 0