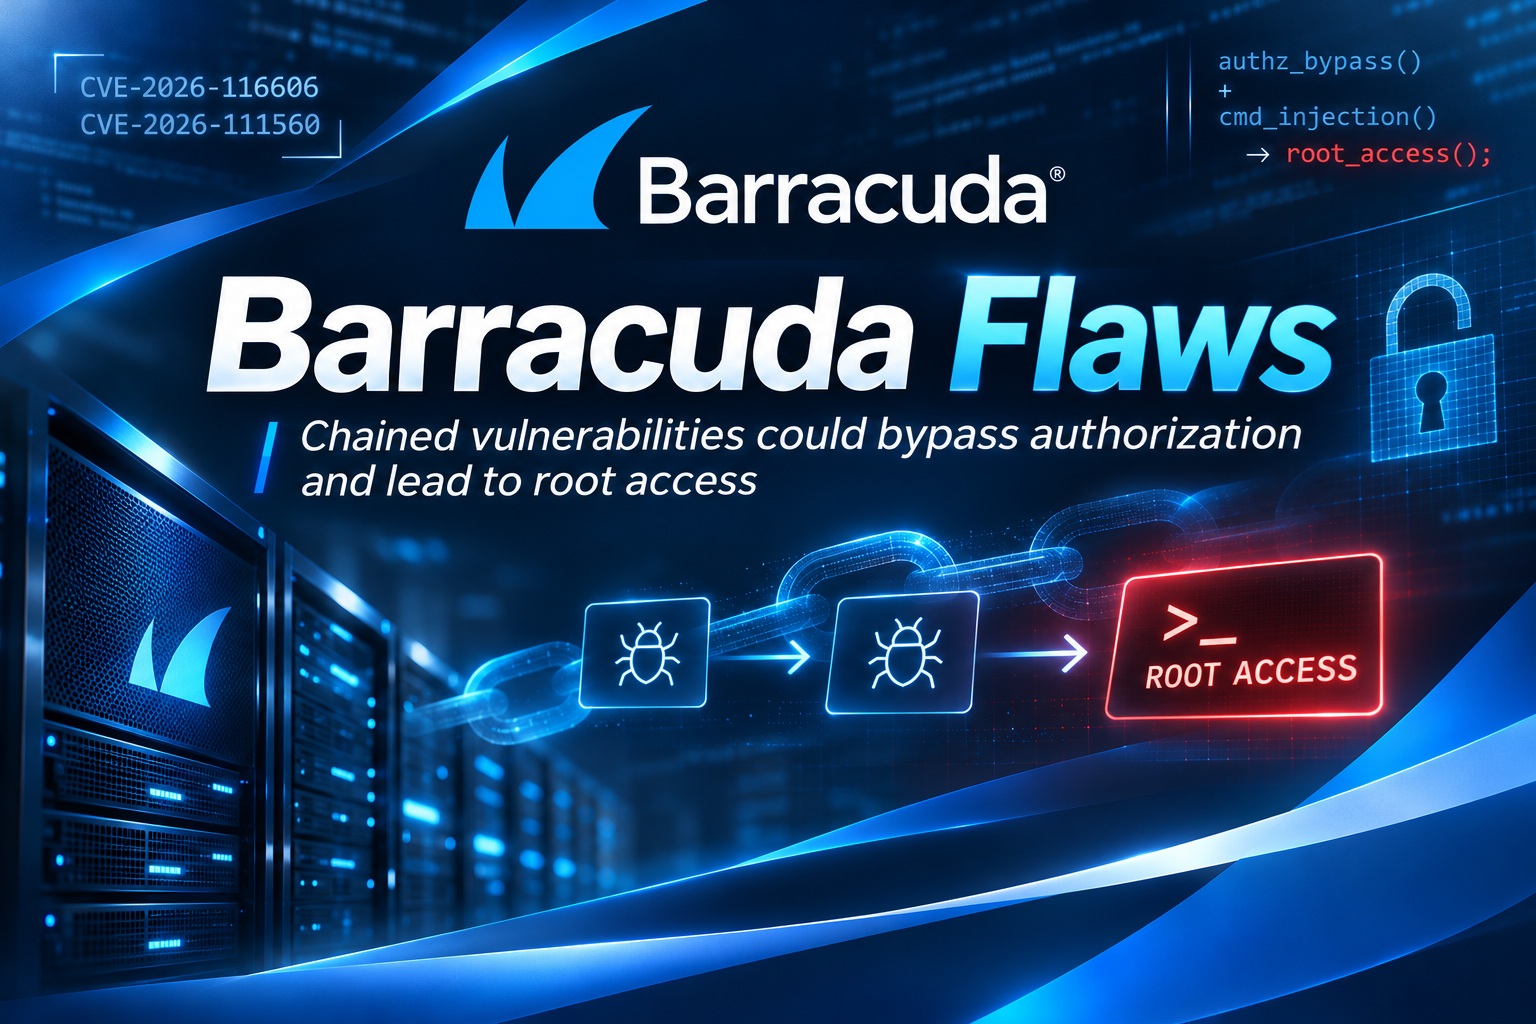
Barracuda has disclosed two serious vulnerabilities affecting several of its security appliances that could become particularly dangerous when exploited together. By chaining the flaws, an attacker with network access to a vulnerable device's administrative interface could potentially bypass authorisation controls and ultimately obtain root-level access to the appliance. The two vulnerabilities are tracked as CVE-2026-116606 and CVE-2026-111560, with severity scores of 9.3 and 8.6 respectively.
The vulnerabilities do not affect exactly the same products, but the overlap is important because Barracuda Email Security Gateway is vulnerable to both. The company is urging customers to update affected appliances and ensure that administrative interfaces are not unnecessarily exposed to the public internet.
The First Vulnerability Allows Pre-Authentication Authorisation Bypass
The more severe of the two flaws is CVE-2026-116606, which carries a CVSS score of 9.3. Barracuda describes it as a pre-authentication authorisation bypass vulnerability affecting its Email Security Gateway product. Because exploitation occurs before authentication, an attacker does not necessarily need valid administrator credentials before attempting to take advantage of the weakness.
Authorisation controls are supposed to determine what a user is permitted to access or perform after reaching a system. A flaw that allows those controls to be bypassed before authentication can therefore create a particularly dangerous entry point. When combined with another vulnerability capable of executing commands, the security consequences become considerably more serious.
CVE-2026-111560 Is A Command Injection Vulnerability
The second vulnerability, CVE-2026-111560, carries a CVSS score of 8.6 and involves command injection. Successful command injection can potentially allow attacker-controlled input to be interpreted as commands by the underlying operating system rather than being treated only as ordinary application data.
On its own, the vulnerability already represents a significant risk because security appliances typically operate with elevated privileges and sit in important positions within corporate networks. When paired with the authorisation bypass vulnerability, however, Barracuda warns that an attacker could potentially move from unauthorised access to full root-level control of the affected appliance.
The Two Vulnerabilities Can Be Chained Together
Barracuda says the main concern is the ability to combine the two weaknesses into one attack chain. An attacker could first use CVE-2026-116606 to bypass normal authorisation controls and then take advantage of CVE-2026-111560 to execute commands on the affected device.
If successful, that combination could provide root access, which represents the highest level of privilege on the underlying Linux-based system. Root access gives an attacker far more control than compromising an ordinary application account and may potentially allow them to alter configurations, access sensitive information or establish additional persistence on the appliance.
Email Security Gateway Is Exposed To Both Flaws
CVE-2026-116606 specifically affects Barracuda Email Security Gateway, making it the product most directly exposed to the complete vulnerability chain. Email Security Gateway appliances are typically positioned between an organisation's mail environment and external email traffic, making them especially sensitive infrastructure.
Compromising an email security appliance could potentially give an attacker access to systems responsible for inspecting and filtering corporate email. Even without considering the specific capabilities of these vulnerabilities beyond Barracuda's disclosure, root access to any security appliance should be treated as a serious incident because the device itself occupies a trusted position within the network.
The Command Injection Flaw Affects Several Barracuda Products
CVE-2026-111560 has a wider product impact than the authorisation bypass vulnerability. Barracuda says the affected products include:
• Email Security Gateway
• Load Balancer Application Delivery Controller
• Message Archiver
• WAF Control Center
• Web Application Firewall
• Web Security Gateway
Organisations using any of these products should therefore verify their software versions even if they do not operate Email Security Gateway. The full two-vulnerability chain may not apply in exactly the same way across every product, but the command injection flaw itself remains serious enough to require remediation.
Administrative Interface Access Is Required
Barracuda notes that successful exploitation requires the attacker to have access to the administrative interface of the affected product. This is an important limitation because systems whose management interfaces are restricted to trusted internal networks are considerably less exposed than appliances that allow administrative connections directly from the internet.
However, administrative interfaces can sometimes become publicly accessible unintentionally through firewall rules, remote management configurations or infrastructure changes made over time. Organisations should therefore verify actual network exposure rather than assuming the interface is private simply because that was the original design.
Internet-Exposed Management Interfaces Carry Greater Risk
Security appliances often need remote administration, but exposing their management portals directly to the internet creates an additional attack surface. Automated scanners can discover internet-facing interfaces relatively quickly, especially once information about a vulnerability becomes public.
Attackers do not necessarily need to know an organisation uses a particular Barracuda appliance in advance. They can potentially scan large portions of the internet looking for systems that respond like the vulnerable product. Restricting access therefore removes a significant number of potential attackers before they can even reach the vulnerable functionality.
Barracuda Recommends Restricting Administrative Interfaces
One of Barracuda's primary recommendations is to ensure administrative interfaces are accessible only from trusted internal networks. Organisations should avoid allowing unrestricted internet access to management portals unless there is an unavoidable operational requirement.
Administrative access can instead be placed behind a VPN, dedicated management network or other controlled access path. These approaches reduce the number of systems capable of connecting to the interface while still allowing authorised administrators to perform their work.
Network Access Controls Should Also Be Reviewed
Barracuda additionally recommends using appropriate network access controls to limit exposure. Firewalls, access-control lists and network segmentation can all help ensure that only approved systems or IP addresses are able to reach management services.
This is especially important for security infrastructure because compromised management interfaces can give attackers control over devices trusted by other parts of the organisation. Restricting the management plane can therefore significantly reduce the likelihood that an external attacker can exploit the vulnerabilities in the first place.
Security Appliances Should Not Be Assumed To Be Secure By Default
Products such as email gateways, web application firewalls and secure web gateways are purchased specifically to improve security, which can sometimes create a false sense that the appliances themselves require less protection. In reality, they are still complex networked systems containing operating systems, web applications and management services that can contain vulnerabilities.
Their position in the network can actually make them more attractive targets. A compromised security appliance may have access to traffic, configuration information or trusted network segments that ordinary endpoints do not. Security teams therefore need to patch and monitor defensive infrastructure with the same urgency applied to public-facing servers.
Root Access Represents A Serious Compromise
Root is the highest privilege level on Unix and Linux systems. If an attacker successfully obtains root access, they can generally perform actions far beyond those available to ordinary users or even many administrative accounts within the application itself.
Depending on the appliance architecture, root-level compromise could potentially allow attackers to manipulate system files, alter services or interfere with security configurations. This is why the combination of an authorisation bypass and command injection vulnerability is particularly dangerous even though exploitation requires access to the management interface.
Patch Management Is The Main Long-Term Fix
Barracuda is advising customers to ensure affected products are running the latest available firmware versions and have received all applicable security patches. Network restrictions can reduce immediate exposure, but they do not remove the vulnerable code from the appliance.
The permanent remediation is therefore to update the software. Organisations should include these appliances in their normal vulnerability-management programme rather than treating firmware updates as occasional maintenance tasks performed only when new features are required.
Some Appliances May Need Multiple Firmware Updates
Barracuda warns that systems running firmware several releases behind the current version may require more than one update. This is an important operational detail because some appliances cannot jump directly from a very old firmware release to the newest one.
Administrators should review the supported upgrade path before beginning maintenance. Skipping required intermediate versions could cause the update to fail or potentially create compatibility problems, so following the vendor's upgrade sequence is important.
Do Not Assume An Update Was Successful Until It Is Verified
Installing firmware should be followed by verification that the appliance actually reached the expected version. Security teams should check the running firmware after maintenance and confirm that the relevant security fixes are present.
This becomes particularly important in environments containing multiple appliances because one overlooked device may remain vulnerable even after the organisation believes patching has been completed. Central asset inventories can help identify every affected system and record its remediation status.
Older Appliances Deserve Extra Attention
Devices that have been running for many years are more likely to be several firmware releases behind, particularly if administrators avoided updates because the appliances appeared stable. Those systems may require additional maintenance windows to move through intermediate releases before reaching a fully patched version.
Older installations can also be easier to overlook if they were deployed by previous IT teams or reside in less frequently reviewed network segments. A vulnerability announcement like this is therefore a useful opportunity to confirm that the organisation still has a complete inventory of its Barracuda appliances.
Administrative Interfaces Should Be Audited From Outside The Network
One practical way to verify exposure is to check which management services are reachable from outside the organisation. Firewall configuration documentation may say the interface is restricted, but actual network testing provides stronger assurance.
Security teams should confirm whether administrative ports respond from untrusted networks and close any access that is not explicitly required. Exposure can sometimes appear following temporary troubleshooting changes that were never reversed.
VPN Access Is Preferable To Direct Internet Management
Where administrators genuinely need remote access, requiring them to connect through a secured VPN before reaching the management interface provides another protective layer. The appliance management portal itself no longer needs to be exposed directly to every internet address.
Multi-factor authentication should also be used wherever the surrounding access infrastructure supports it. Even though the vulnerabilities themselves are not necessarily dependent on stolen credentials, strengthening remote administration reduces other opportunities for compromise.
Security Appliances Should Live On Dedicated Management Networks
Larger organisations may benefit from placing appliance administration interfaces on dedicated management networks that ordinary users and production systems cannot access directly. Administrators can then reach them only through controlled jump hosts or privileged workstations.
This architecture dramatically reduces the number of devices capable of interacting with management services. If an ordinary employee workstation becomes compromised, the attacker should not automatically gain a network path towards the organisation's email gateway or web application firewall administration interface.
Segmenting The Management Plane Limits Attack Opportunities
Network segmentation is valuable because security incidents often begin on systems unrelated to the eventual target. Attackers may compromise one workstation and then search internally for other reachable services.
If management interfaces are accessible from ordinary user networks, the attacker may eventually discover them. Separating administrative infrastructure helps prevent an initial endpoint compromise from turning into control of critical network appliances.
Command Injection Bugs Can Be Particularly Dangerous On Appliances
Command injection vulnerabilities are serious in almost any application, but their impact can be magnified on dedicated appliances. These systems often contain privileged backend services specifically designed to modify network rules, configuration files or security policies.
An attacker able to inject operating-system commands may therefore gain access to capabilities far beyond what the normal web interface exposes. This is why even a vulnerability requiring authenticated or management-interface access should not be dismissed as low risk.
Security Devices Can Become High-Value Attack Targets
Attackers increasingly target the products organisations depend on for security. Firewalls, VPN gateways, email security systems and other edge appliances are attractive because they are frequently internet-connected and operate with high privileges.
Compromising one can potentially provide a foothold that bypasses some of the organisation's normal endpoint protections. Security teams should therefore assume that defensive products themselves will be actively targeted and maintain them accordingly.
Email Security Gateways Need Particular Attention
The Email Security Gateway deserves additional attention because it is affected by both disclosed vulnerabilities. Email systems are already among the most heavily targeted parts of corporate infrastructure because so many attacks begin through phishing or malicious attachments.
A compromised email security appliance could undermine trust in a system specifically deployed to inspect inbound and outbound messages. Organisations running Barracuda Email Security Gateway should therefore prioritise checking firmware versions and management-interface exposure immediately.
WAF Products Also Sit In Sensitive Network Positions
Barracuda's Web Application Firewall and WAF Control Center are affected by the command injection vulnerability. Web application firewalls often sit directly in front of important internet-facing applications, placing them in a particularly sensitive position within the infrastructure.
A vulnerability in the security layer protecting web applications can create an unusual situation where the defensive system becomes part of the attack surface. Keeping those appliances fully updated is therefore just as important as patching the web servers behind them.
Load Balancers Are Critical Infrastructure Too
The affected Load Balancer Application Delivery Controller may also play an essential role in directing traffic between application servers. If a load balancer becomes unavailable or compromised, several services behind it can potentially be affected simultaneously.
This makes redundancy and secure administration particularly important. Appliances that appear to perform only an infrastructure function can still become critical points of failure within the wider environment.
Message Archivers May Contain Valuable Information
Barracuda Message Archiver systems can potentially hold large collections of historical communications. Even though the disclosed issue concerns command injection rather than a specific data-exposure vulnerability, any compromise of such an appliance should be treated seriously because of the information it may contain or access.
Security teams should understand what data each appliance stores and which other services it can communicate with. That knowledge helps determine the potential impact if an appliance is compromised.
Web Security Gateways Also Need Updating
Web Security Gateway deployments are another affected product category. These appliances can play an important role in controlling and monitoring users' web access, which means they may interact with large amounts of network traffic and organisational policy information.
As with the other affected devices, access to administrative interfaces should be tightly restricted and firmware should remain current. Organisations should not wait for evidence of exploitation before addressing a known command injection vulnerability in trusted infrastructure.
Monitoring Should Continue Even After Patching
Applying updates reduces the vulnerability risk, but organisations should still review logs for unusual administrative activity. Suspicious logins, unexpected configuration changes or unfamiliar commands could indicate that an appliance was targeted before it was patched.
If internet exposure existed while the device was vulnerable, administrators may want to perform a deeper review rather than simply updating and moving on. Patching prevents future exploitation of the known flaw but does not automatically undo actions already taken by an attacker.
Unexpected Configuration Changes Should Be Investigated
Security appliances generally have relatively stable configurations, so unexplained changes deserve attention. New administrator accounts, altered access rules or unexpected networking settings can be indicators that someone gained unauthorised control.
Organisations should maintain backups or configuration histories where supported so legitimate settings can be compared against the current state. This can help identify changes that would otherwise be difficult to notice.
Asset Inventory Is Essential During Vulnerability Response
When a vulnerability affects several different products, organisations need an accurate inventory to determine which systems require action. Searching manually through network documentation can take too long if records are outdated.
A good asset-management process should identify device type, firmware version, network location and management-interface exposure. That information allows security teams to quickly prioritise the systems presenting the greatest immediate risk.
Internet-Facing Appliances Should Be Prioritised First
If patching every device immediately is impossible, systems with administrative interfaces exposed to untrusted networks should receive the highest priority. Barracuda specifically notes that organisations whose management interfaces are not internet-exposed are less vulnerable to the described attack path.
That does not mean internally accessible appliances can remain unpatched indefinitely. Internal attackers or compromised endpoints may still reach them, but limiting external exposure significantly reduces the number of potential attack sources.
Defence In Depth Remains Important
The incident demonstrates why security should never depend on one control. Strong authentication helps, but an authorisation bypass may circumvent it. A firewall can restrict access, while patched firmware removes the vulnerable functionality entirely.
Network segmentation, logging, access restrictions and software updates all provide different layers of defence. If one layer fails, another can still reduce the likelihood or impact of compromise.
Final Thoughts
Barracuda's disclosure of CVE-2026-116606 and CVE-2026-111560 highlights a particularly dangerous vulnerability combination affecting important security infrastructure. CVE-2026-116606 is a critical pre-authentication authorisation bypass vulnerability rated 9.3 and specifically affects the Email Security Gateway, while CVE-2026-111560 is an 8.6-rated command injection vulnerability affecting six Barracuda product families.
The biggest concern is what happens when the vulnerabilities are chained. An attacker able to reach the administrative interface of a vulnerable Email Security Gateway could potentially bypass authorisation and then exploit command injection to obtain root-level access to the appliance.
Barracuda recommends restricting administrative interfaces to trusted internal networks, applying appropriate network access controls and ensuring all affected appliances are running current firmware with every security patch installed. Systems several firmware releases behind may require multiple sequential updates before reaching a fully patched version.
For organisations running Barracuda security appliances, the most important step is therefore straightforward: verify what devices you have, confirm whether their management interfaces are exposed, and update them before the security product designed to protect your network becomes the attacker's way into it.






Comments 0