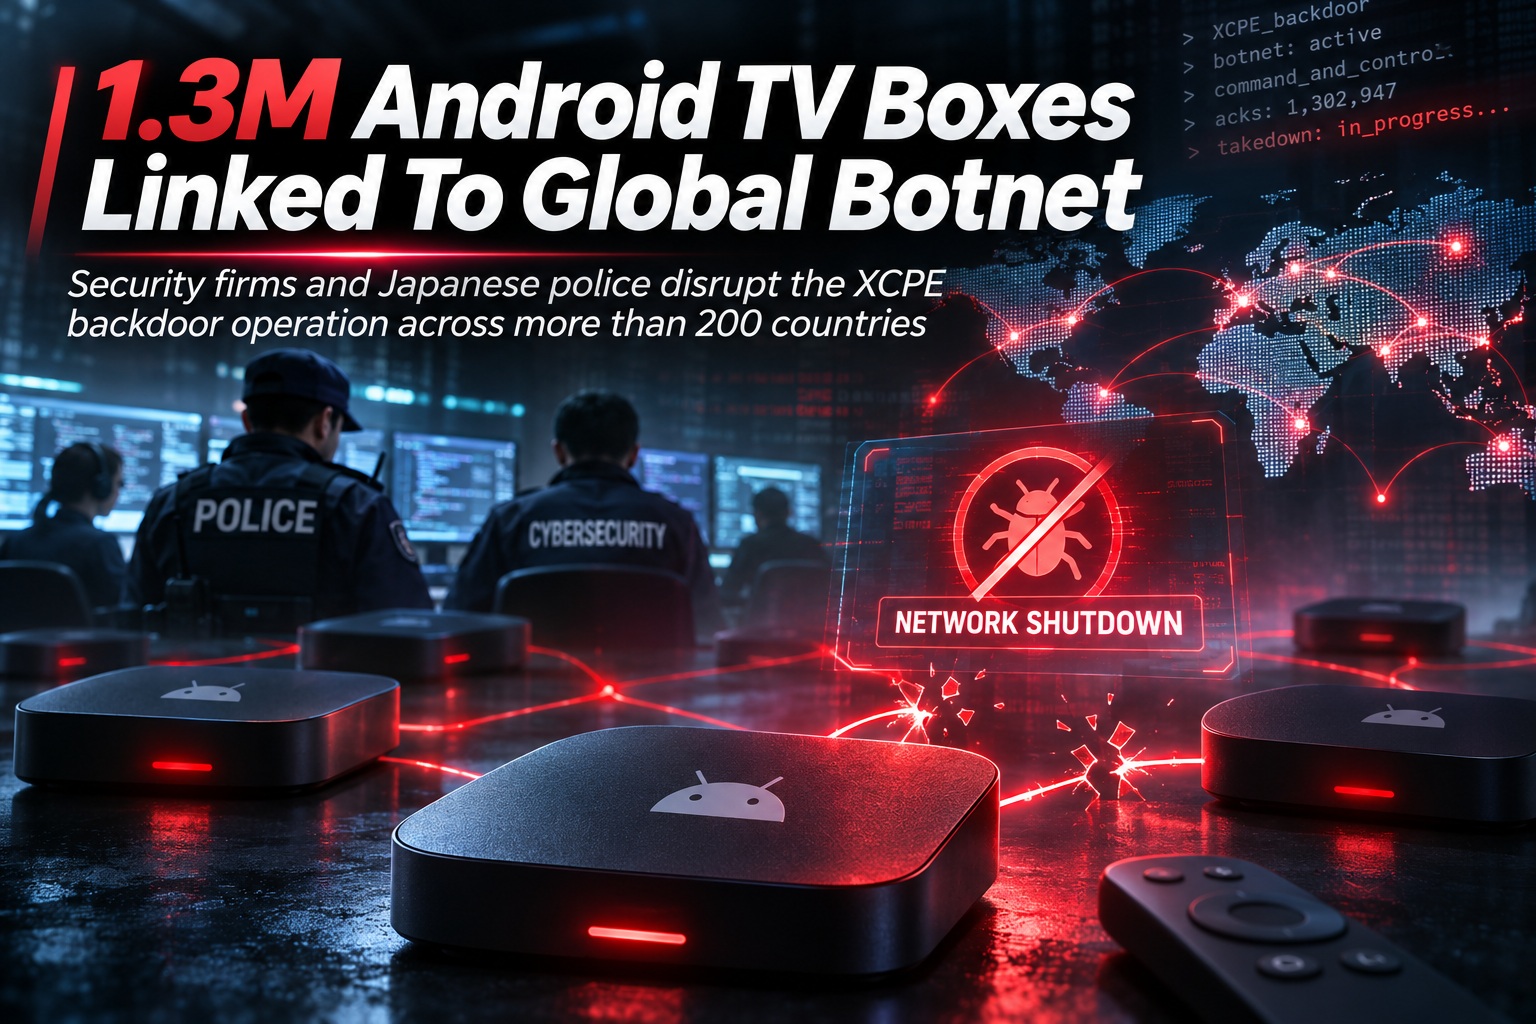
A major international operation involving Japan's National Police Agency and several private cybersecurity companies has disrupted XCPE, a backdoor used to build a botnet containing more than 1.3 million compromised Android devices across over 200 countries. The operation involved Google, Lumen, Human Security, Plume, Synthient and TrendAI, combining law-enforcement coordination with technical infrastructure takedowns. Investigators believe the malware was deliberately embedded into certain Android devices before they ever reached customers, turning ordinary TV boxes and projectors into part of a criminal network as soon as they were connected to the internet.
XCPE Was Allegedly Built Into Device Firmware
Google's Threat Intelligence Group said it assesses with high confidence that the XCPE backdoor and botnet were intentionally developed, deployed and operated for financial gain by Videostrong Technology, a hardware manufacturer based in Shenzhen, China. The company produces Android-based devices including TV boxes and projectors, and Google alleges that the backdoor was deliberately included inside device firmware rather than being added later through a conventional malware infection. This meant customers could purchase what appeared to be a normal consumer device while unknowingly receiving hardware that already contained remote-control capabilities.
Customers Could Be Compromised Simply By Connecting The Device
The danger emerged as soon as buyers connected the affected devices to their home networks. According to Google, the preinstalled backdoor allowed operators to transform the devices into part of proxy networks that routed criminal traffic through the customer's internet connection. The legitimate homeowner's IP address could therefore be used to disguise malicious activity, making the traffic appear as though it originated from an ordinary residential connection. Victims did not need to install suspicious applications or click malicious links because the compromise was already present before the device was switched on.
Botnet Operators Could Sell Access To Criminal Affiliates
Google says Videostrong allegedly sold access to the compromised devices to criminal affiliates, allowing third parties to install additional malware modules. This created a flexible criminal platform rather than a botnet limited to one specific activity. Different affiliates could potentially use the same underlying device population for separate operations, depending on which modules they installed. The business model effectively turned millions of unsuspecting consumers' devices and internet connections into infrastructure that could be rented or exploited for profit.
The Malware Pretended To Be A Normal Management Agent
TrendAI found that the firmware included a preinstalled management agent that appeared to be an ordinary remote-management component. In reality, the software connected back to external infrastructure controlled by the operators. This kind of disguise can make malicious behaviour difficult for ordinary users to recognise because remote-management software is not unusual on Android-based consumer devices. Unless someone specifically examined the network traffic or firmware, there may have been little visible indication that the device was part of a botnet.
GitHub Was Used To Deliver Updates
The management agent reportedly retrieved updates from a GitHub page, allowing the operators to change or expand its capabilities after devices had already been sold. Using a legitimate service such as GitHub can make malicious infrastructure less obvious because connections to popular development platforms may not immediately appear suspicious. Attackers frequently abuse trusted online services because blocking them outright can interfere with legitimate applications. In this case, the update mechanism helped the operators maintain control over devices already deployed inside homes and businesses.
MQTT Infrastructure Provided Full Remote Control
TrendAI also discovered that the devices connected to a Message Queuing Telemetry Transport, or MQTT, server controlled by the operators. MQTT is a legitimate lightweight messaging protocol commonly used by Internet of Things devices, but it can also provide efficient command-and-control communications when abused by attackers. Through this connection, the XCPE operators could reportedly install or remove applications, modify system settings and push updates remotely. That level of control effectively turned each compromised Android box into a remotely managed computer inside the victim's network.
Millions Of IP Addresses Were Linked To The Operation
Between 3 June and 1 October, TrendAI recorded more than 3.8 million distinct residential and mobile IP addresses connecting to infrastructure associated with the operation. That figure does not necessarily mean 3.8 million separate infected devices because individual devices can appear under multiple IP addresses over time, particularly on mobile or dynamically assigned residential connections. Nevertheless, it demonstrates the enormous scale and geographical reach of the operation. A botnet spanning more than 200 countries gives operators access to residential internet connections across a huge portion of the world.
The Confirmed Botnet Included More Than 1.3 Million Android Devices
Investigators identified more than 1.3 million Android devices as part of the XCPE botnet. Android TV boxes are particularly attractive to attackers because many low-cost devices remain powered on continuously and receive little security attention once installed. Users may keep them connected to their televisions for years without ever checking whether firmware updates are available. That long operating lifespan can provide attackers with persistent access if the device ships compromised from the factory.
Home Internet Connections Are Valuable To Cybercriminals
Residential proxy networks are valuable because traffic originating from home broadband connections often appears more trustworthy than traffic from obvious data centres or hosting providers. Criminals can use those residential IP addresses to disguise automated activity, evade geographical restrictions or make malicious traffic harder to identify. A compromised Android box can therefore generate value even if attackers never access personal files stored on the device. The victim's internet connection itself becomes the asset being exploited.
Users May Notice Nothing Unusual
One reason botnets involving consumer devices can remain active for long periods is that they do not necessarily need to make the infected device visibly malfunction. A TV box can continue streaming videos and running applications while simultaneously forwarding traffic or receiving commands in the background. If the malware avoids consuming excessive bandwidth or processing power, users may have little reason to suspect anything is wrong. This makes firmware-level compromises particularly difficult to detect without specialised monitoring.
The Coalition Targeted Command-And-Control Infrastructure
The disruption effort did not focus only on individual infected devices. The participating organisations also targeted the command-and-control domains used by the criminal affiliates to manage their malware modules. Removing or redirecting these domains can prevent compromised devices from receiving instructions even if the malicious software remains installed. Disrupting the communications infrastructure is often one of the fastest ways to weaken a large botnet without needing physical access to every infected device.
The Takedown Could Affect Far More Than 1.3 Million Devices
Google estimates that disabling the affiliate command-and-control infrastructure could sever malicious access to at least 10 million additional compromised devices. This is because the criminal affiliates involved reportedly used other distribution channels in addition to XCPE. Their malware modules may therefore exist on devices that were compromised through completely different methods. Taking their central command infrastructure offline can potentially disrupt those infections as well, making the impact of the operation significantly larger than the core XCPE botnet.
Criminal Affiliates Had Multiple Distribution Channels
The wider ecosystem demonstrates how modern botnets increasingly operate like businesses with separate suppliers, distributors and customers. One group may provide compromised devices, another may develop malware modules and others may purchase access for specific criminal campaigns. Taking down one component does not necessarily eliminate every participant because affiliates can have additional ways to distribute their malware. This modular structure makes cybercrime infrastructure more resilient and difficult to dismantle permanently.
Google Has Cut Ties With Videostrong
Following the investigation, Google said it had terminated its relationship with Videostrong. The manufacturer has also been prohibited from producing devices that come with Google applications preloaded. Losing access to Google's ecosystem could have serious commercial consequences because legitimate Android certification and bundled Google services are important selling points for many consumer devices. The action also sends a clear message that manufacturers may face platform-level consequences when devices are found to contain deliberately malicious firmware.
Videostrong Has Not Publicly Responded
Videostrong reportedly did not immediately respond to requests for comment regarding the allegations. As a result, the public account of the operation currently comes primarily from the security companies and law-enforcement partners involved in the disruption. Google's assessment explicitly attributes intentional development and operation of the XCPE botnet to the manufacturer, making the allegation considerably more serious than a case where a supply-chain attacker secretly modified devices without the vendor's knowledge. Any eventual response from the company would therefore be important in understanding how it addresses those claims.
XCPE Is Connected To The Broader BadBox Ecosystem
Researchers say XCPE belongs to the same broader criminal ecosystem as BadBox 2.0, another huge Android botnet previously associated with compromised TV boxes and similar consumer electronics. BadBox 2.0 reportedly infected more than 10 million devices before Human Security, Google and TrendAI disrupted the operation in March 2025. The similarity shows that low-cost Android hardware continues to provide fertile ground for large-scale botnet activity. Disrupting one campaign does not necessarily eliminate the underlying criminal networks or the insecure supply chains that enable them.
BadBox 2.0 Demonstrated The Same Supply-Chain Problem
BadBox campaigns attracted attention because many devices arrived infected rather than being compromised after users installed something malicious. Supply-chain attacks are especially dangerous because traditional advice such as "do not click suspicious links" does little to protect someone from malware already present in the product they purchased. The user may behave perfectly safely and still become part of a botnet. This shifts more responsibility towards manufacturers, distributors and the platforms certifying consumer hardware.
Cheap Android TV Boxes Can Carry Greater Security Risk
Android TV boxes are available from countless manufacturers, often at extremely low prices and through online marketplaces with little information about long-term support. Some run heavily modified Android builds and may never receive meaningful security updates after leaving the factory. Others may contain software from multiple third-party suppliers whose security practices are difficult for buyers to assess. Saving money on the initial purchase can therefore come with risks that are almost impossible for ordinary consumers to evaluate beforehand.
Firmware Malware Is Harder To Remove Than A Bad App
When malware is installed as an ordinary Android application, removing the offending app or resetting the device may sometimes solve the problem. Firmware-level backdoors are much more difficult because they can be part of the operating system image itself. A factory reset may simply restore the compromised firmware and reactivate the same malicious components. Replacing the firmware safely may require technical knowledge or a clean image that the manufacturer never provides.
Factory Resets May Not Be Enough
Users who suspect that a device belongs to a supply-chain botnet should therefore not assume that performing a factory reset guarantees safety. If the malicious management agent is built into the firmware, the reset process may reinstall exactly the same compromised software. In those situations, replacing the hardware may be considerably safer than attempting to clean it. This is particularly true for inexpensive devices where trusted firmware images and long-term security support are unavailable.
The Device Can Also Create Risk For The Home Network
An infected TV box does not exist in isolation because it normally sits on the same home network as laptops, smartphones, cameras and other connected devices. Even if XCPE's primary purpose is building a proxy network, any device with persistent remote-control capability deserves concern because it provides attackers with a foothold inside the local environment. Network segmentation can help reduce this risk by keeping untrusted smart devices away from computers and storage containing sensitive information. Unfortunately, most home networks place everything on the same Wi-Fi network by default.
IoT Devices Should Ideally Be Isolated
People with routers that support guest networks or dedicated IoT networks can reduce exposure by placing inexpensive smart devices on a separate network. The TV box may still access the internet, but it cannot communicate freely with laptops, NAS devices or other sensitive systems on the main network. This does not remove malware from the device, but it limits what that malware can potentially reach. Network isolation is becoming increasingly valuable as homes accumulate more internet-connected hardware from different vendors.
Consumers Should Prefer Certified Devices
One practical way to reduce risk is choosing Android TV devices from reputable manufacturers with recognised certification and a clear software-update policy. Google-certified products do not guarantee that vulnerabilities will never exist, but legitimate certification creates additional requirements and accountability compared with obscure devices running unofficial Android builds. Consumers should be cautious when products advertise access to popular streaming services while providing little information about the manufacturer or software support. Extremely cheap hardware can sometimes hide costs that are paid through privacy and security rather than money.
Preinstalled Malware Is A Very Different Threat
Most cybersecurity advice assumes attackers need to convince users to download something malicious. Preinstalled backdoors completely change that model because the compromise happens before the user even owns the product. The first network connection effectively activates infrastructure already under someone else's control. That makes supply-chain security one of the most difficult cybersecurity challenges because the victim has almost no opportunity to prevent the initial infection.
Manufacturers Need Stronger Supply-Chain Oversight
Hardware vendors need to know exactly what software is being included in firmware before products ship. Devices often contain components from chipset vendors, subcontractors and third-party software providers, creating a complicated chain where malicious or insecure code can be introduced. Proper code signing, build verification and independent firmware auditing can help detect unauthorised changes. If Google's assessment of XCPE is correct, however, this case goes beyond accidental supply-chain compromise and involves deliberate inclusion of the backdoor itself.
Retailers And Marketplaces Also Have A Role
Online marketplaces can make it extremely easy for unknown manufacturers to sell inexpensive Android devices worldwide. When one product is discovered to contain malicious firmware, marketplaces should be able to identify affected models quickly and prevent further sales. Buyers should also receive clear notifications if hardware they purchased is later associated with a security incident. The global scale of the XCPE botnet demonstrates how quickly compromised consumer electronics can spread when distributed through international retail channels.
Residential Proxy Abuse Can Affect Innocent Users
Victims whose internet connections are used as proxies may face consequences even if attackers never steal anything directly from them. Websites may block their IP addresses after detecting suspicious activity, while online services can mistakenly associate the household connection with fraud or automated abuse. In more serious situations, investigators may initially see the victim's IP address in logs associated with criminal traffic. The user becomes part of the attack infrastructure without ever knowingly participating.
Bandwidth And Performance Could Also Be Affected
Proxy activity can consume internet bandwidth, potentially reducing connection performance for legitimate users. The impact may be difficult to notice if attackers deliberately limit traffic to avoid drawing attention. Over time, however, a large number of background connections could still affect data usage, particularly for households with capped plans. Unusual network traffic from a TV box that appears idle can therefore be worth investigating.
Router Logs Can Sometimes Reveal Suspicious Behaviour
Technically experienced users may be able to identify unusual connections by examining router logs, DNS queries or network-monitoring tools. A simple streaming device repeatedly connecting to unfamiliar servers even when not in active use may deserve further investigation. However, distinguishing malicious traffic from legitimate advertising, analytics and update services can be difficult because modern smart devices communicate with many external domains. This is another reason why preventing compromised hardware from entering the network is preferable to trying to detect it afterwards.
The Operation Shows The Scale Of Modern Botnets
More than 1.3 million confirmed devices across over 200 countries demonstrates how enormous botnets built from inexpensive consumer electronics can become. Each individual device may have limited computing power, but together they create a huge distributed network of residential connections. Botnet operators value scale because large numbers of geographically diverse devices can support proxy services, automated abuse and other criminal activity. The victims effectively provide electricity, hardware and internet connectivity for the attacker's infrastructure.
Law Enforcement Needs Private-Sector Cooperation
The disruption also demonstrates why dismantling global botnets requires cooperation between governments and technology companies. Law enforcement may provide legal authority and investigative coordination, while security firms possess telemetry capable of identifying infected devices and command infrastructure across the internet. Google, Lumen, Human Security, Plume, Synthient and TrendAI each contributed capabilities that would be difficult for one organisation to replicate alone. Botnets operating in hundreds of countries cannot realistically be tackled by one national police agency acting independently.
Domain Disruption Can Be Extremely Effective
Taking control of or disabling command-and-control domains can rapidly weaken a botnet because infected devices lose their instructions. This technique does not necessarily remove the malware, but it prevents operators from communicating with large portions of the compromised fleet. Researchers can sometimes redirect those connections towards sinkhole infrastructure to measure infections and prevent further malicious commands. Long-term recovery still requires replacing or cleaning the infected devices, but command disruption can immediately reduce harm.
The Devices May Remain Compromised After The Takedown
One important limitation is that disrupting the botnet infrastructure does not magically remove XCPE from every affected Android box. Devices containing the backdoor may remain technically compromised even if the original operators can no longer reach them through the disabled servers. Future infrastructure changes or additional malware already present on the device could still create risk. Owners of confirmed affected hardware should therefore not assume that the law-enforcement action has permanently made their devices safe.
Old Devices Can Remain A Problem For Years
Consumer electronics often remain in use far longer than smartphones or computers. A cheap TV box may sit behind a television for five or ten years as long as streaming applications continue working. If those products stop receiving security updates almost immediately after purchase, vulnerabilities and malicious components can remain active for years. This long lifecycle helps explain why botnets involving IoT and entertainment devices can remain persistent even after researchers repeatedly disrupt their infrastructure.
BadBox And XCPE Show A Recurring Pattern
The link between XCPE and the BadBox ecosystem suggests that this is not simply one isolated incident involving one unusual batch of devices. Security researchers have repeatedly discovered compromised Android TV boxes being used as proxy nodes or botnet infrastructure. Each disruption removes part of the ecosystem, but the financial incentives remain strong enough for new campaigns to appear. The underlying combination of inexpensive hardware, weak security and global distribution continues to create opportunities for attackers.
Users Should Check The Manufacturer Of Their Android Boxes
Anyone using a low-cost Android TV box or projector should know who actually manufactured the device and whether the vendor provides legitimate firmware updates. Products sold under unfamiliar brands may sometimes originate from the same original equipment manufacturers and differ only in external branding. This makes identifying potentially affected hardware more complicated than checking one retail brand name. Device model, firmware version and manufacturer information can therefore be important when security advisories emerge.
Disconnecting Suspicious Hardware Is The Safest Immediate Step
If a device is confirmed or strongly suspected to contain a firmware-level backdoor, disconnecting it from the network is the safest immediate action. Continuing to use compromised hardware simply because the command-and-control infrastructure has been disrupted leaves unnecessary uncertainty. Replacing the device with a trusted alternative may be more practical than attempting to determine whether every malicious component has been removed. Consumer entertainment hardware is rarely worth risking the security of an entire home network.
Final Thoughts
The disruption of XCPE reveals just how dangerous compromised consumer hardware can become when malicious software is embedded before the device ever reaches its owner. More than 1.3 million Android devices across over 200 countries were reportedly enrolled into the botnet, with security researchers observing millions of residential and mobile IP addresses associated with the operation.
Google says it believes with high confidence that Videostrong Technology deliberately developed and embedded the XCPE backdoor into firmware and sold access to compromised devices to criminal affiliates. Once customers connected affected TV boxes or projectors to the internet, operators could remotely install applications, alter settings and use the victim's residential connection as part of proxy networks.
The coalition of Japan's National Police Agency, Google, Lumen, Human Security, Plume, Synthient and TrendAI has now disrupted key infrastructure supporting the operation. Google estimates that taking down affiliate command-and-control systems could also sever access to at least 10 million additional compromised devices outside the core XCPE network.
However, infrastructure disruption does not necessarily remove the malicious firmware from affected hardware. Users should remain cautious with unknown Android TV boxes, particularly products with unclear manufacturers or no reliable security-update history.
The most unsettling part of XCPE is that victims did not necessarily make any mistake. They could purchase a device, connect it normally and unknowingly become part of a criminal botnet from the moment it went online.






Comments 0