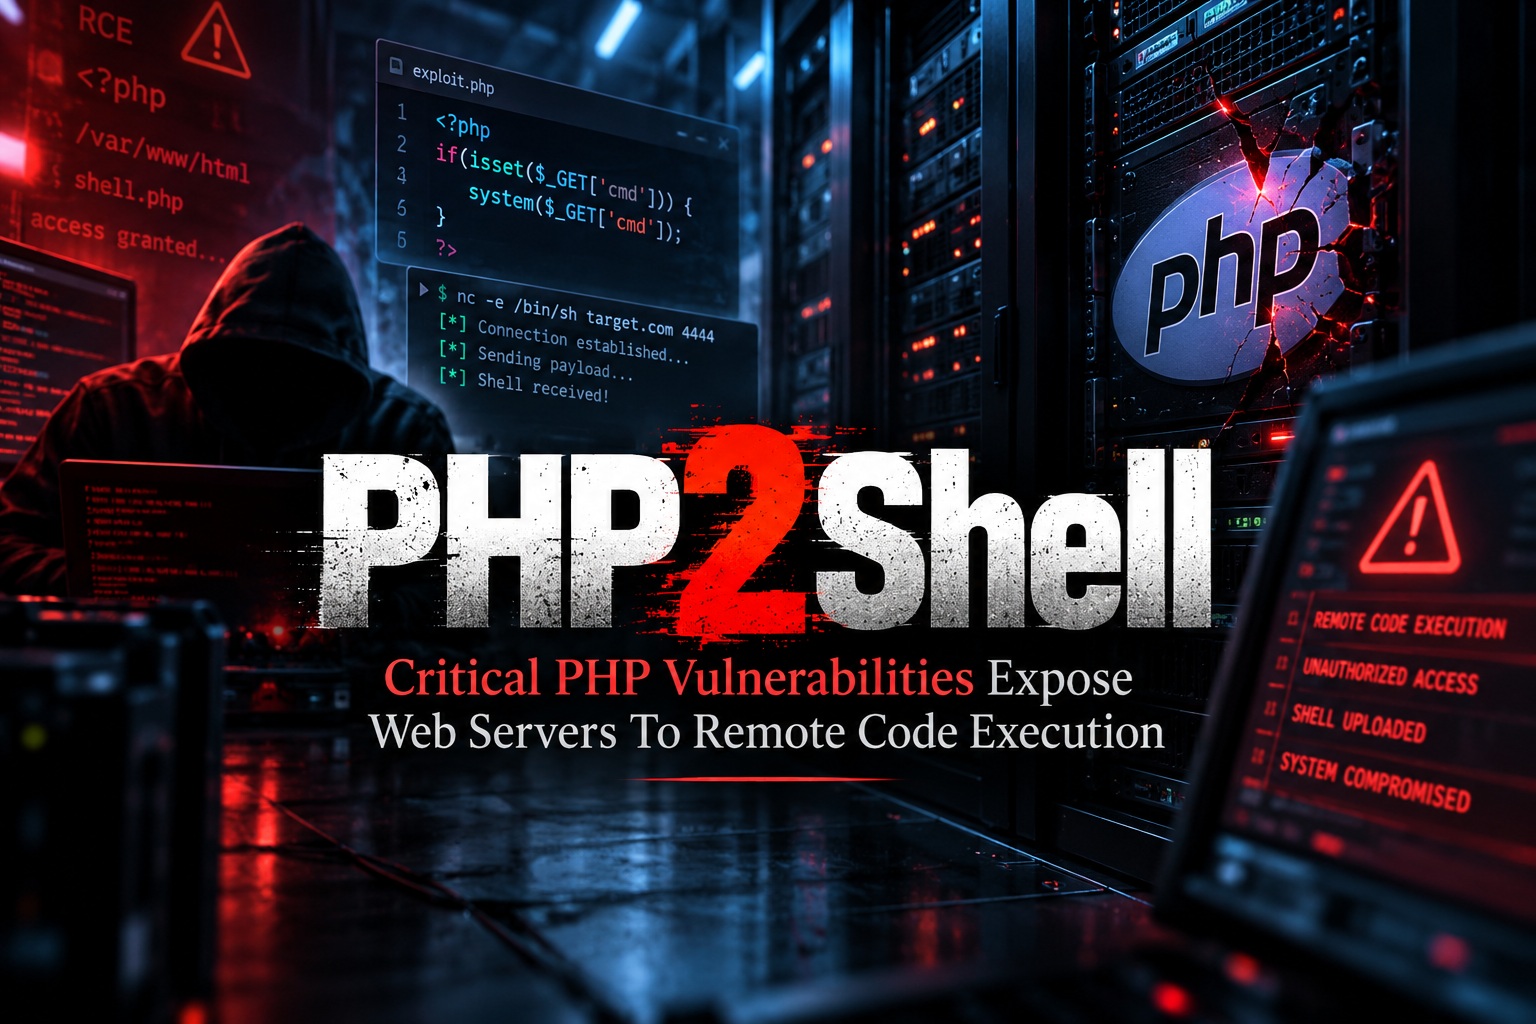
The PHP development team has released urgent security updates addressing two critical vulnerabilities collectively referred to as PHP2Shell. The flaws affect PHP itself rather than a particular content management system, plugin or web application, which means any server relying on a vulnerable PHP installation could potentially be exposed.
Tracked as CVE-2026-109618 and CVE-2026-109619, both vulnerabilities carry a CVSS v4.0 score of 9.2 out of 10. Successful exploitation could allow an unauthenticated attacker to execute arbitrary commands on a vulnerable web server, potentially leading to complete server compromise. Public proof-of-concept exploit code is already available, and exploitation attempts have reportedly been observed, making immediate patching particularly important.
The Vulnerabilities Exist Inside PHP Core
One of the most serious aspects of PHP2Shell is where the vulnerabilities exist. These are not weaknesses inside WordPress, Drupal, Joomla or another PHP-based application. Instead, the flaws affect PHP's core request-handling functionality, which processes incoming web requests before the application itself handles them.
That means a website can be carefully secured at the application level and still remain vulnerable if the underlying PHP runtime has not been updated. Custom PHP applications are affected by the same underlying risk because the vulnerability exists beneath the application layer.
Any internet-facing server using an affected PHP release should therefore be treated as potentially vulnerable regardless of which framework or CMS it is running.
CVE-2026-109618 Involves Out-Of-Memory Corruption
The first vulnerability, CVE-2026-109618, is an Out-of-Memory corruption issue affecting PHP's core request handling. An unauthenticated attacker can exploit the flaw using specially crafted multipart/form-data requests designed to exhaust PHP's available memory while request information remains only partially initialised.
Under vulnerable conditions, this memory handling problem can be abused to execute arbitrary code on the server. Because no login credentials are required, an attacker only needs network access to the vulnerable PHP service and the ability to send the specially crafted request.
For an internet-facing web server, that significantly increases the practical risk.
CVE-2026-109619 Is A Use-After-Free Vulnerability
The second critical flaw, CVE-2026-109619, is a Use-After-Free vulnerability involving stale global state within PHP's request-handling process. The issue occurs when specially crafted requests cause a PHP worker to reuse request data that has already been freed from memory.
An unauthenticated attacker may be able to manipulate this behaviour and eventually execute arbitrary code on the vulnerable server. The vulnerability can also involve PHP's Session Upload Progress functionality, which is enabled by default.
Because the flaw can be triggered across a sequence of specially constructed requests, administrators should not assume that disabling an individual web application feature will automatically remove the underlying PHP vulnerability.
Attackers Do Not Need An Account
Both vulnerabilities are particularly dangerous because exploitation does not require authentication. An attacker does not need a legitimate website account, administrative credentials or previous access to the server.
Instead, malicious requests can be sent directly to the PHP service. If the underlying PHP version is vulnerable and the deployment configuration permits exploitation, the attacker may be able to execute commands using the privileges of the affected PHP process.
From there, the impact could extend well beyond the original website.
Successful Exploitation Could Lead To Full Server Compromise
Remote code execution is one of the most serious classes of software vulnerability because it allows attackers to run their own instructions on the affected system. Depending on the privileges available to the PHP process and the server's configuration, attackers could potentially install malware, modify website files, access databases or create persistent backdoors.
A compromised web server can also become a stepping stone into other systems connected to the same network. Credentials stored in application configuration files could potentially provide access to databases, email systems, cloud services or APIs.
This makes PHP2Shell a server-security issue rather than merely a website problem.
Sensitive Process Memory May Also Be Exposed
The advisory warns that successful exploitation could potentially expose sensitive information contained within process memory. This may include credentials, API keys and other secrets temporarily present while PHP handles requests.
Even if an attacker does not immediately obtain full administrative control of the operating system, access to these secrets could enable additional attacks. Database credentials, API tokens or cloud keys stolen from memory may provide access to systems far beyond the original server.
Organisations should therefore consider credential exposure when responding to suspected exploitation, not simply whether website files were modified.
Multiple PHP Deployment Types Are Potentially At Risk
PHP2Shell is not limited to one particular web-server configuration. The advisory identifies multiple PHP deployment methods that may be affected, including:
• PHP-FPM
• Apache with mod_php
• php-cgi
• FrankenPHP
• LiteSpeed
Any PHP installation serving web requests should therefore be reviewed against the affected versions.
The risk is considered particularly serious for Apache with mod_php, where a demonstrated exploit requires only an unauthenticated request and can run before application code is executed.
Apache With mod_php Faces The Highest Risk
Apache installations using mod_php deserve immediate attention. In this configuration, the vulnerable PHP processing happens directly inside the Apache request flow, allowing exploitation before WordPress, Joomla, Drupal or another application gets an opportunity to inspect the request.
This means application-level security controls may provide little or no protection against the attack. A web application firewall or other upstream protection may help reduce exposure in some environments, but the advisory makes clear that updating PHP is the only safe response.
Administrators running Apache with mod_php should therefore prioritise these systems during remediation.
PHP 8.5 Users Need Version 8.5.12
All PHP 8.5 versions earlier than 8.5.12 are affected by PHP2Shell.
The fixed release is:
Any server running PHP 8.5.11 or earlier should be upgraded immediately.
Administrators should confirm the actual PHP version being used by the web server rather than relying solely on what a control panel or package manager appears to show.
PHP 8.4 Requires Version 8.4.27
For the PHP 8.4 branch, all versions before 8.4.27 are affected.
The recommended fixed version is:
This means PHP 8.4 environments should be updated even if they were recently patched for unrelated vulnerabilities. PHP2Shell requires the specific fixed release or a later supported update.
After upgrading, PHP worker processes and relevant web services should be restarted so that the patched runtime is actually loaded.
PHP 8.3 Requires Version 8.3.36
All PHP 8.3 versions before 8.3.36 are vulnerable.
The fixed release is:
This branch is particularly important because PHP 8.3 remains widely deployed across production hosting environments. Administrators using shared hosting, VPS platforms or managed servers should verify whether their provider has already deployed the update.
If the server is self-managed, updating should be treated as an emergency maintenance task.
PHP 8.2 Requires Version 8.2.35
For PHP 8.2, affected versions include everything before 8.2.35.
The fixed version is:
However, PHP 8.2 is approaching end-of-life on 31 December 2026. Organisations still using this branch should therefore treat the security update as a short-term requirement while also planning migration to a newer supported PHP release.
Remaining on a branch approaching end-of-life increases the likelihood that future vulnerabilities will become harder to address.
PHP 7.4, 8.0 And 8.1 Are End-Of-Life
The situation becomes much more serious for older PHP branches. PHP 7.4, PHP 8.0 and PHP 8.1 are all listed as affected, but these versions are already end-of-life.
There is no official fixed release for these branches.
Organisations running these versions should therefore upgrade to a supported PHP generation rather than waiting for an official security patch that will not arrive.
Depending on the environment, an LTS vendor or operating-system distributor may provide backported fixes, but these should be treated as temporary measures rather than a long-term solution.
PHP 7.3 And Earlier Have No Fix Available
The advisory is even more concerning for PHP 7.3 and earlier, extending back through PHP 5.x.
All of these versions are considered affected and end-of-life.
There is no fix available through the official PHP project.
Any production website still using these branches should be migrated as soon as possible. Continuing to operate an internet-facing PHP 5.x or similarly outdated environment now carries an especially significant security risk.
There Is No Complete Mitigation
The PHP project has stated that there are no complete mitigations for PHP2Shell. Updating to a fixed PHP version is considered the only safe response.
This is particularly important because organisations may be tempted to rely on firewall rules, configuration changes or application-level security controls while delaying the upgrade. Those measures may reduce exposure in certain circumstances, but they should not be considered equivalent to installing the patched runtime.
The underlying vulnerability remains inside PHP itself until the software is updated.
Internet-Facing Servers Should Be Patched First
Organisations with many PHP systems should prioritise remediation according to exposure. Publicly accessible servers should come first because attackers can reach them directly from the internet.
Websites, API endpoints, customer portals and public applications deserve immediate attention. Internal PHP systems should also be patched, but the externally accessible systems represent the most urgent attack surface.
Attackers frequently scan the internet automatically after proof-of-concept code becomes available, meaning delays can quickly increase exposure.
Restart PHP Workers After Updating
Installing a patched package is not necessarily enough if old PHP processes continue running in memory. Administrators should restart the relevant services and worker processes after completing the upgrade.
Depending on the server architecture, this may involve restarting PHP-FPM, Apache, LiteSpeed or another service hosting the PHP runtime.
Without a restart, existing workers may continue using the previously vulnerable PHP binary until they are recycled naturally.
A post-update version check should also be performed to confirm that requests are actually being processed by the patched release.
Shared Hosting Customers Should Check With Their Provider
Organisations using shared hosting may not have direct control over the PHP runtime. In these environments, the hosting provider is responsible for installing patched PHP packages on the underlying infrastructure.
Customers should verify which PHP version their website is currently using and confirm that it has been updated to a fixed version. If the provider continues offering unsupported branches such as PHP 5.6 or PHP 7.x, users should understand that those versions may no longer receive official PHP security fixes.
Where possible, applications should be tested and migrated towards supported PHP releases.
Legacy Applications Create A Difficult Upgrade Problem
The greatest challenge will likely involve applications that depend on outdated PHP versions. Older CMS installations, custom applications and abandoned plugins may not function correctly on modern PHP releases.
This creates a dangerous situation where the server cannot safely remain on the old PHP branch, but upgrading PHP may break the application.
In those cases, organisations need to treat application modernisation as a security priority rather than merely a development improvement. Running an unsupported PHP version on an internet-facing server is becoming increasingly difficult to justify.
Third-Party Products Embedding PHP May Also Be Affected
PHP2Shell is not limited to traditional websites. Third-party products that embed PHP internally may also be vulnerable if they ship with affected versions.
This means organisations should review appliances, management platforms and commercial software that may use PHP behind the scenes. Administrators may not even realise PHP is present because the application exposes only its own interface.
Software vendors should be checked for advisories confirming whether their products contain vulnerable PHP components and whether updates are available.
Public Proof-Of-Concept Code Raises The Urgency
The availability of public proof-of-concept code significantly changes the risk. Attackers no longer need to independently discover how the vulnerability works before attempting exploitation.
PoC code can often be adapted into automated scanning and exploitation tools. Once that happens, attackers can search large numbers of internet-facing systems quickly.
Because exploitation attempts have already reportedly been observed, administrators should assume that vulnerable servers may already be receiving malicious requests.
Review Logs For Signs Of Exploitation
Patching should be the first priority, but organisations may also want to review web-server and application logs for unusual activity. Repeated malformed multipart requests, abnormal PHP worker crashes or suspicious requests occurring shortly before unexpected server behaviour may deserve investigation.
Because successful exploitation may result in arbitrary command execution, security teams should also look for unexpected processes, modified files, unusual outbound connections or new user accounts.
If compromise is suspected, simply installing the patch may not be enough. An attacker who already gained access could have established persistence before the vulnerability was fixed.
Potentially Exposed Credentials Should Be Rotated
If there is evidence that a server was exploited, organisations should assume that sensitive process memory and local configuration files may have been exposed.
Credentials stored on the server should therefore be reviewed and rotated where appropriate. This may include database passwords, API keys, cloud credentials, SMTP passwords and application secrets.
Session tokens and other authentication material may also need to be invalidated depending on what the affected application handles.
Incident response should consider the wider environment rather than treating the PHP server as an isolated system.
Legacy PHP Is Now An Even Bigger Security Liability
PHP2Shell highlights the growing danger of running applications on unsupported PHP branches. Older environments may remain operational for years because businesses are reluctant to modify systems that still appear to work.
The problem is that software can continue functioning perfectly while becoming increasingly insecure.
A PHP 5.x website may still serve pages exactly as it did a decade ago, but the absence of official security fixes means newly discovered vulnerabilities can leave administrators with no safe patching path.
At some point, application compatibility needs to give way to basic security requirements.
Final Thoughts
PHP2Shell represents a serious threat because the vulnerabilities exist inside the PHP core itself and can potentially be exploited by unauthenticated attackers before a web application has any opportunity to intervene. CVE-2026-109618 and CVE-2026-109619 both carry a critical CVSS v4.0 score of 9.2, and successful exploitation can result in arbitrary remote code execution and potentially complete control of the affected web server.
PHP has released fixed versions 8.5.12, 8.4.27, 8.3.36 and 8.2.35, while older end-of-life branches do not receive an official fix. PHP 7.4, 8.0 and 8.1 require migration or vendor-provided interim backports, while PHP 7.3 and earlier — including PHP 5.x — have no official fix available.
With public proof-of-concept exploit code available and exploitation attempts already reported, delaying remediation creates unnecessary risk. Internet-facing systems should be upgraded first, PHP services should be restarted after patching, and organisations still relying on unsupported PHP versions should treat migration as an urgent security requirement rather than a future maintenance project.
PHP2Shell is therefore not simply another CMS vulnerability that can be solved by updating a plugin. It affects the runtime underneath the entire application stack, which makes the safest response very straightforward: identify every affected PHP server and update it immediately.






Comments 0