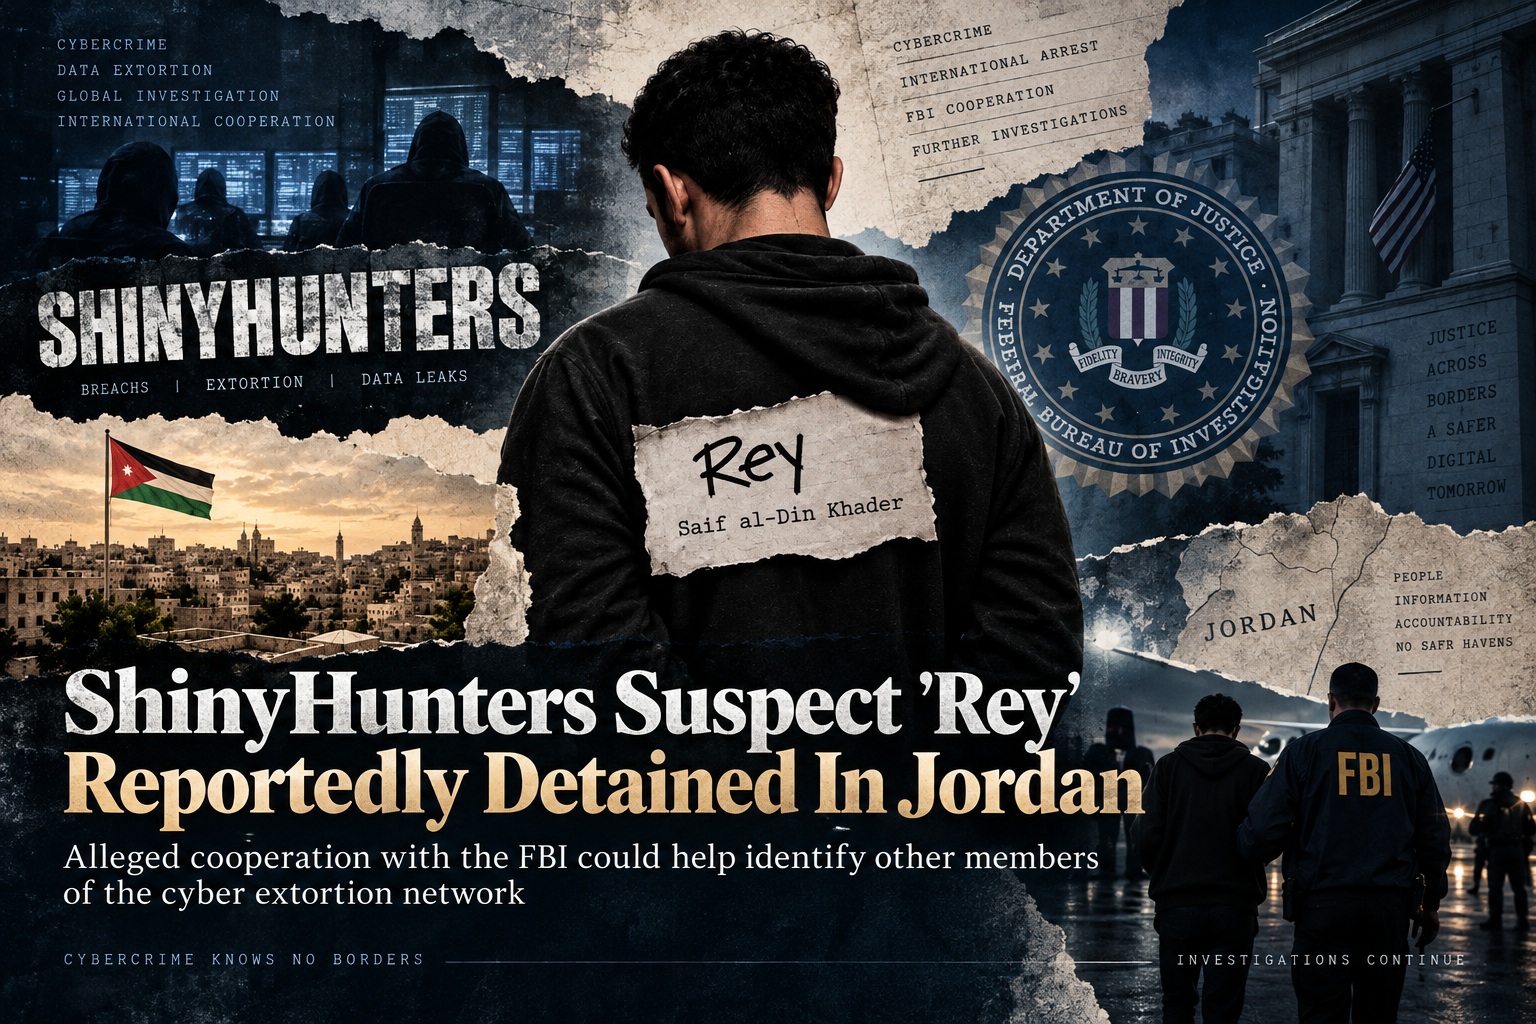
A suspected member of the ShinyHunters digital extortion ecosystem, known online as "Rey" and "ReyXBF", has reportedly been detained by authorities in Jordan and is said to be cooperating with U.S. law enforcement. The individual, identified in reports as Saif al-Din Khader, was allegedly taken into custody on 29 September 2026. His cooperation is now believed to be helping investigators identify other people connected to ShinyHunters and related cybercrime operations.
The development marks another significant step in the widening law-enforcement campaign against individuals linked to ShinyHunters. It follows other recent arrests and comes at a time when authorities appear to be increasing pressure on the broader network of hackers, extortionists and social engineers associated with the brand.
Rey Reportedly Helping Investigators Identify Other Members
According to reports citing people familiar with the matter, Khader is cooperating with the U.S. Federal Bureau of Investigation and other law-enforcement agencies. One source described his assistance as critical to ongoing efforts to identify and arrest additional members of the group. If accurate, that cooperation could give investigators valuable insight into the identities, infrastructure and working relationships behind ShinyHunters.
For cybercrime investigations, cooperation from an insider can be particularly important because these groups frequently operate through pseudonyms, encrypted communications and distributed online infrastructure. Even where authorities seize servers or accounts, linking online identities to real individuals can remain difficult. Someone familiar with the group's internal structure may therefore provide context that technical evidence alone cannot easily establish.
Rey Has Been Linked To Several Cybercrime Groups
Khader is not a previously unknown figure in underground cybercrime reporting. In November 2025, independent security journalist Brian Krebs identified him as one of three administrators associated with Scattered LAPSUS$ Hunters, sometimes shortened to SLH or SLSH. That group has been described as an overlap or loose combination involving individuals associated with Scattered Spider, LAPSUS$ and ShinyHunters.
Before that, Rey was reportedly involved with the Hellcat ransomware operation and served as an administrator of its data-leak website after the group appeared in late 2024. He was also linked to a more recent incarnation of BreachForums, one of the online forums historically used for trading stolen data and discussing cybercrime. Khader had previously claimed that he had been cooperating with law enforcement since at least June 2025.
Another Suspected ShinyHunters Figure Was Recently Arrested
The reported detention in Jordan comes shortly after authorities arrested a 24-year-old man in Amsterdam over alleged involvement in malicious cyber operations linked to the group. Although authorities did not initially disclose his identity, independent reporting later identified him as Pepijn van der Stap, a reformed hacker who had been working as an offensive security lead at Dutch company Neo Security.
A ShinyHunters spokesperson subsequently denied having any connection with van der Stap. Nevertheless, the arrest prompted the FBI to signal that investigators were actively pursuing additional leads. FBI director Kash Patel said further arrests remained possible as teams continued examining information obtained through the investigation.
FBI Says More Arrests Could Follow
The FBI has publicly indicated that the investigation remains active and that the recent arrests may generate new intelligence. Patel stated that investigative teams were working with partners to pursue additional leads and later said more arrests could be on the table. This suggests that authorities are treating the current developments as part of a broader operation rather than isolated enforcement actions.
Brett Leatherman, assistant director of the FBI's cyber division, also described one of the arrested suspects as an alleged leader within the wider operation. He warned remaining participants that arrests and infrastructure seizures often create new opportunities for investigators because seized systems can expose communications, relationships and identities that were previously hidden.
Group Allegedly Linked To More Than 140 Breaches
U.S. authorities have alleged that the wider cybercrime operation was involved in breaches affecting more than 140 organisations. Investigators also claim that the group and its associates obtained at least US$70 million through extortion payments. The attackers are said to frequently target third-party vendors and cloud-based platforms, stealing sensitive information before threatening to publish it unless victims pay.
This business model reflects the shift many cybercrime groups have made away from relying solely on ransomware encryption. In some cases, simply stealing sensitive information can provide enough leverage for extortion. Organisations may face pressure not only because of operational disruption, but also because of the regulatory, reputational and legal consequences that can follow a major data leak.
ShinyHunters Recently Targeted Other Cybercrime Infrastructure
The ShinyHunters name has also appeared in several unusual recent incidents involving both law-enforcement and criminal infrastructure. The group reportedly hijacked the darknet website belonging to another cybercriminal operation, Cl0p, by exploiting an unpatched vulnerability in Grav CMS. It has also claimed responsibility for compromising the FBI's apply.fbijobs.gov portal and stealing around three terabytes of sensitive information.
ShinyHunters has claimed that its objective in the FBI incident was not financial. Instead, the group said it wanted to pressure the agency into changing what it described as inaccurate allegations about ShinyHunters and its supposed relationship with The Com. That loosely connected cybercrime ecosystem has been associated with activities including social engineering, phishing, SIM swapping, extortion, sextortion, swatting, kidnapping and physical violence.
ShinyHunters Has Evolved Beyond A Single Group
Security researchers tracing the history of ShinyHunters have argued that the name now represents more than a traditional hacking group. Its lineage has been linked to earlier extortion-focused operations including TheDarkOverlord and GnosticPlayers, while the ShinyHunters name itself became publicly recognised around April or May 2020. Over time, the brand survived arrests, indictments, forum seizures and changes in personnel.
Researchers have described ShinyHunters as increasingly resembling a reusable criminal brand and business model rather than a fixed organisation with a permanent membership list. Different individuals may contribute specialised roles, including initial access, social engineering, recruitment, amplification and monetisation. That modular structure helps explain why the name can continue appearing even after prominent participants are arrested.
A Network That Can Regenerate After Arrests
The resilience of groups such as ShinyHunters presents a major challenge for law enforcement. Removing a single administrator or infrastructure node does not necessarily dismantle the entire operation because other participants can replace missing roles. New forums, aliases and partnerships can emerge quickly, particularly when the underlying methods remain profitable.
This is why insider cooperation can become especially valuable. Investigators may be able to move beyond the visible infrastructure and identify how different actors are connected, who performs particular functions and which online identities belong to the same individuals. If Rey is indeed providing this level of information, the consequences could extend beyond one arrest.
Final Thoughts
The reported detention of Saif al-Din Khader in Jordan could become an important development in the international investigation surrounding ShinyHunters and related cybercrime networks. His alleged cooperation with the FBI may help authorities identify additional participants and better understand how the group operates behind its constantly changing online identities. Combined with the recent Amsterdam arrest, the case suggests that law enforcement is placing increasing pressure on individuals believed to be connected to the wider ecosystem.
At the same time, ShinyHunters has shown considerable resilience over the years, surviving arrests, forum takedowns and changes in leadership while continuing to reappear under familiar branding. That makes the current investigation significant not simply because another suspected member may be in custody, but because cooperation from insiders could provide authorities with a clearer picture of the network behind the name. Whether that ultimately leads to a broader wave of arrests remains to be seen.






Comments 0