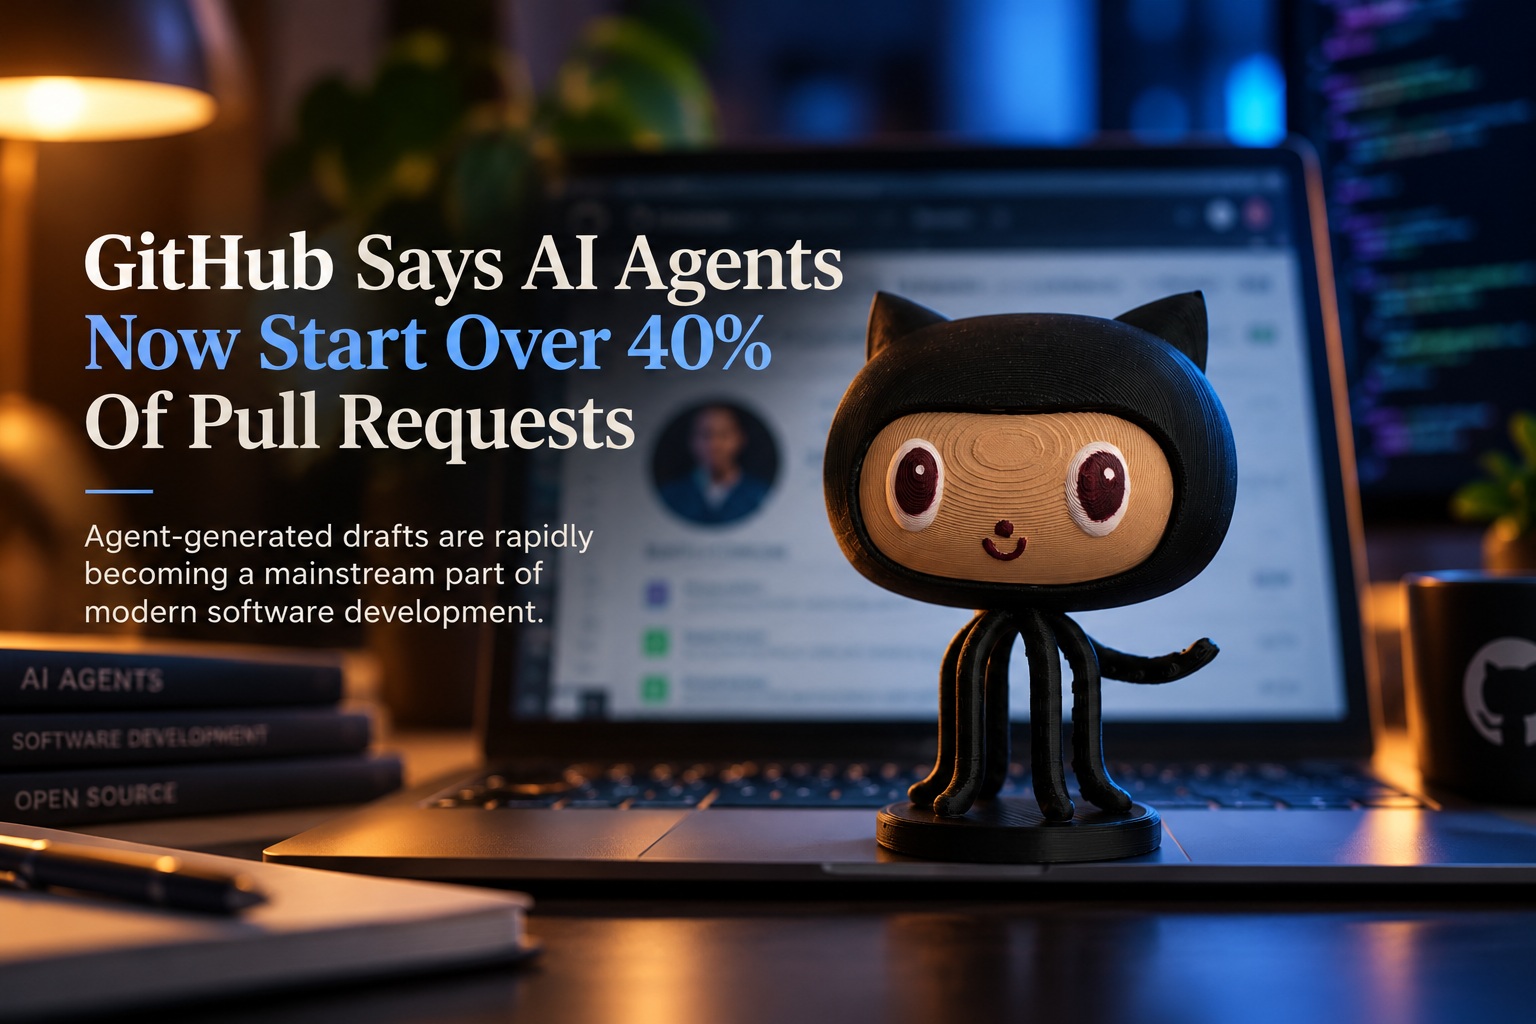
Artificial intelligence is rapidly becoming a bigger part of software development workflows on GitHub, with the company reporting that more than 40% of pull requests created in September 2026 began with an AI agent-generated draft. That figure is significantly higher than the 17% recorded in March, showing just how quickly agent-assisted development has expanded across the platform.
According to GitHub's Octoverse 2026 report, AI agents started around 110 million pull requests in September alone, roughly six times the volume recorded in March. The numbers are based on GitHub's own detection of agent activity across the platform and cover selected months within the reporting period from 1 October 2025 through 30 September 2026.
AI Agents Are Handling Larger Development Tasks
GitHub's data suggests AI agents are increasingly being used for more than simple one-file fixes. Around 87% of pull requests started by agents modified multiple files, compared with 79% of pull requests where no agent involvement was detected.
That difference suggests developers are increasingly assigning broader development tasks to AI systems. Instead of asking an assistant to generate one function or make one isolated change, agents are being trusted with work that spans multiple parts of a codebase.
This fits with the wider shift towards agentic development tools that can independently inspect repositories, make changes and prepare pull requests for human review.
Agent-Started Pull Requests Are Being Merged Faster
GitHub also reported an increase in the percentage of agent-started pull requests merged within two weeks. That figure rose from 83% in February to 90% in September.
For pull requests without detected AI-agent involvement, the rate remained relatively stable at around 86% over the same period. However, GitHub's figures describe how quickly pull requests were merged rather than whether the resulting code was necessarily better.
A faster merge does not automatically mean higher-quality code, so the numbers are more useful as indicators of workflow speed than software quality.
Copilot Users Are Increasingly Turning To Agentic Features
GitHub Copilot itself is also becoming much more agent-oriented. Among monthly active Copilot users, 55% were using agentic capabilities, up from 35% a year earlier.
This suggests developers are moving beyond traditional autocomplete and chat-based assistance towards tools capable of taking on more independent tasks. Instead of merely suggesting code, agents can inspect context, make changes and generate work for developers to review.
The shift reflects a broader trend across AI-assisted software development, where the assistant increasingly behaves like a collaborator rather than a simple coding helper.
Copilot Cloud Agent Usage Jumped 230%
Usage of GitHub's cloud-based Copilot agent reportedly increased 230% year over year. This feature allows developers to assign tasks to an AI agent and let it work independently rather than supervising every individual step.
Agent chat usage also grew by 85% over the same period. Together, those figures show that developers are becoming more comfortable delegating work rather than using AI only for inline suggestions.
The more capable these tools become, the more software development may shift towards reviewing and coordinating AI-generated work rather than manually writing every change from scratch.
Copilot Projects Expands Multi-Repository Agent Work
GitHub recently introduced Copilot Projects in public preview, giving developers a way to coordinate AI agents across multiple repositories. The feature is designed to help teams manage larger development efforts rather than treating each repository or task in isolation.
Developers can provide context from several sources, including code repositories, design files, Slack conversations and meeting notes. They can also choose which models and tools Copilot should use while completing the assigned work.
This broader project context could make agents significantly more useful on complex software where decisions depend on information spread across several systems.
Developers Still Review The Agent's Output
Even when agents perform the initial work, developers remain responsible for reviewing the resulting changes. Copilot Projects allows users to inspect agent-generated pull requests before those changes are merged.
That review step remains important because autonomous agents can still misunderstand requirements, introduce bugs or make technically valid changes that do not match the intended design.
The workflow therefore increasingly becomes one where AI prepares the work and humans validate whether it should actually enter the codebase.
AI-Assisted Code Review Is Growing Quickly
GitHub also reported strong growth in AI-assisted code review. Usage of these tools increased by more than 90% year over year, suggesting developers are using AI not only to write code but also to inspect it.
Automated review can help identify potential bugs, security concerns or inconsistencies before a human reviewer begins examining the changes. This can reduce some of the repetitive work involved in large pull requests.
However, human review remains especially important for architectural decisions, security-sensitive changes and logic that requires deeper understanding of business requirements.
GitHub Advanced Security Usage Also Grew More Than 90%
GitHub Advanced Security saw similarly strong adoption, growing by more than 90% year over year. The platform provides tools aimed at identifying vulnerabilities and security issues directly within software development workflows.
This growth reflects how security is becoming more integrated into the development process rather than being treated as something checked only after software is complete.
Combining automated security scanning with AI-assisted remediation could make it easier for development teams to identify and fix issues much earlier.
Stacked Pull Requests Are Becoming More Popular
GitHub's Octoverse report also highlighted growing use of stacked pull requests, which allow large changes to be divided into smaller related pull requests that can be reviewed independently.
More than 264,000 developers had used the feature by September. GitHub introduced stacked pull requests in public preview in July before making them generally available on 6 October.
The approach can make complicated changes easier to review because developers do not have to examine one enormous pull request containing every related modification at once.
Repositories Using Stacked Pull Requests Merged More Code
During the preview period, repositories using stacked pull requests reportedly recorded a 9% increase in merged code compared with peer repositories.
GitHub also said more than two-thirds of its top 1% of repositories now use stacked pull requests and have seen around a 5% improvement in time to merge.
However, these figures do not prove that stacked pull requests alone caused the improvements. Teams adopting the feature may differ in other ways from repositories that do not use it.
The results are therefore best viewed as GitHub's observed correlation rather than a guaranteed productivity gain.
Smaller Pull Requests Can Make Reviews Easier
The concept behind stacked pull requests is relatively straightforward. Large development work is separated into smaller logical pieces, with each pull request building on the one before it.
Reviewers can focus on one part of the change at a time rather than trying to understand hundreds or thousands of changed lines simultaneously. This can make feedback more precise and reduce the cognitive load involved in reviewing complicated work.
For teams already struggling with large pull requests, the workflow can make collaboration more manageable.
Copilot Code Review Max Uses Multiple AI Agents
GitHub expanded its AI review capabilities further on 28 October by introducing Copilot Code Review Max in public preview.
The feature uses multiple independent review agents powered by models from different providers. These agents examine the same pull request separately before another aggregation agent combines their findings into a single review.
Using several models could help surface different classes of problems rather than depending entirely on the strengths and weaknesses of one AI system.
Max Targets More Complex Code Changes
Code Review Max is designed for particularly difficult or sensitive changes, including authentication logic and shared libraries.
Those types of pull requests often require more careful analysis because mistakes can affect security or many different parts of an application. GitHub positions Max above its existing Lite and Balanced review options for situations where developers want a deeper review.
The trade-off is that Max takes longer to complete and consumes more AI credits than the lighter review modes.
Multiple Models Could Improve Review Coverage
Different AI models may notice different issues in the same code. One might focus on security risks while another identifies logic errors or maintainability problems.
Running independent review agents therefore gives GitHub an opportunity to combine several perspectives. The aggregation agent then attempts to remove duplication and present the most useful findings to the developer.
This resembles a software-development version of asking several reviewers to inspect the same pull request independently before comparing notes.
Copilot Approvals Can Now Count Towards Required Reviews
GitHub has also made Copilot approvals generally available. When enabled, an approval generated by Copilot can count towards a repository's required approval rules.
The feature is disabled by default, meaning administrators need to deliberately turn it on. They can also restrict which file paths Copilot is allowed to approve, giving organisations more control over where AI-generated approvals are accepted.
That could allow teams to automate approval for lower-risk changes while keeping sensitive files under mandatory human review.
New Commits Automatically Dismiss Copilot Approval
GitHub includes an important safeguard around AI approvals. If additional commits are pushed after Copilot approves a pull request, that approval is automatically dismissed.
Developers must then request another review before the AI approval can count again. This prevents a pull request from remaining approved after the underlying code has changed.
The same principle is commonly used with human reviews in security-sensitive repositories, where new changes invalidate previous approval.
Dependabot Pull Requests Continue Growing
Automation is also expanding beyond generative AI. Developers merged more than 30 million Dependabot pull requests, approximately twice the volume recorded in 2025.
Dependabot automatically proposes dependency updates, including versions intended to fix known security vulnerabilities. This can reduce the manual work involved in keeping libraries and packages current.
The growth suggests automated maintenance remains an increasingly important part of modern software development.
Agentic Autofix Moves Security Remediation Further
GitHub also made agentic autofix generally available on 15 October. The feature allows developers to assign code-scanning alerts directly to Copilot for investigation and remediation.
Copilot examines the affected code, develops a potential fix and then runs CodeQL again to determine whether the proposed changes actually resolve the security alert.
If validation succeeds, the system opens a draft pull request containing the proposed fix, an explanation of what changed and details about how the result was validated.
Security Fixes Still Go Through Developer Review
Despite the automation, Copilot does not silently merge the security fix. The generated pull request remains a draft for a developer to inspect.
That gives the team an opportunity to confirm the change does not introduce side effects or alter application behaviour unexpectedly.
The workflow is designed to automate investigation and implementation while preserving human responsibility for the final decision.
Up To 25 Security Alerts Can Be Assigned At Once
Developers can assign up to 25 code-scanning alerts to Copilot within a single pull request.
This could significantly reduce the manual effort required to address groups of related vulnerabilities, particularly in larger repositories with extensive security scanning.
The feature currently works with alerts on a repository's default branch and is available to eligible GitHub Enterprise Cloud customers using GitHub Code Security or Advanced Security.
AI Is Moving From Code Generation To Full Development Workflows
The most important trend in GitHub's report is not simply that AI is generating more code. AI agents are increasingly appearing throughout the entire software-development lifecycle.
They can begin pull requests, coordinate tasks across repositories, review code, approve selected changes, investigate security findings and generate fixes.
That represents a significant shift from the early days of AI coding assistants, where the main functionality was autocomplete.
Developers Are Becoming Supervisors Of AI-Generated Work
As agentic tools become more capable, a growing portion of a developer's job may involve directing, reviewing and validating work produced by AI systems.
This does not necessarily reduce the importance of developers. In many cases, it makes engineering judgement more important because someone still needs to determine whether the generated solution is correct, secure and appropriate for the product.
Writing code may become only one part of the role, while reviewing and coordinating automated work becomes increasingly central.
More Pull Requests Do Not Automatically Mean Better Software
The scale of AI-generated pull requests is impressive, but volume should not be confused with quality.
An agent can create a pull request quickly, but that does not guarantee the architecture is sound, the code is maintainable or the change solves the correct problem.
The increase in merge rates also measures workflow speed rather than long-term software reliability.
Teams adopting agentic development will therefore need strong testing, review and governance practices to ensure that faster output does not simply create more technical debt.
AI Could Also Increase Review Work
There is another possible consequence of easier code generation: developers may produce more changes than human reviewers can comfortably inspect.
If agents dramatically increase the number of pull requests, review capacity could become the new bottleneck.
That is likely one reason GitHub is simultaneously investing so heavily in AI-assisted code review. The same technology increasing the volume of changes may also be needed to help teams evaluate them.
The development workflow could therefore become increasingly AI-assisted on both sides of the pull request.
Security Automation May Be One Of The Strongest Use Cases
Agentic autofix may ultimately prove especially valuable because security maintenance often involves repetitive but important work.
A developer may know a dependency or code path contains a vulnerability but still need time to understand the issue, develop a patch and validate it.
AI agents can perform much of that initial investigation automatically while tools such as CodeQL provide an independent validation step.
When combined with human review, this could significantly reduce the time between vulnerability discovery and remediation.
Enterprise Adoption Will Depend On Governance
Larger organisations will still need clear policies around what AI agents are allowed to do.
Automatically approving a low-risk configuration change may be acceptable, while allowing AI to approve authentication code or financial logic may not be.
File-level restrictions, required human approvals and audit trails will therefore remain important as agentic development expands.
The most successful teams are likely to be those that match the amount of AI autonomy to the risk of the task.
Agentic Development Is Becoming Normal Rather Than Experimental
The rise from 17% to more than 40% of pull requests beginning with agent-generated drafts in only a few months suggests AI agents are moving quickly from experimentation into mainstream development workflows.
At the same time, more than half of active Copilot users are already using agentic features.
This indicates developers are increasingly comfortable handing off meaningful pieces of work rather than simply asking AI for individual coding suggestions.
The shift is happening much faster than many traditional development tools evolved.
Final Thoughts
GitHub's Octoverse 2026 report provides one of the clearest indications yet of how quickly AI agents are becoming part of everyday software development. More than 40% of pull requests in September reportedly began with an AI agent-generated draft, compared with just 17% in March.
GitHub recorded around 110 million agent-started pull requests in September, while 87% of those changes touched multiple files. Agent-started pull requests were also increasingly merged within two weeks, although GitHub correctly notes that merge speed does not tell us whether the resulting code is better.
The wider Copilot ecosystem is moving in the same direction. Cloud agent usage grew 230%, agent chat increased 85%, and more than half of monthly active Copilot users are now using agentic capabilities. GitHub is also expanding AI into review, approval, security remediation and multi-repository project coordination.
At the same time, traditional automation remains important, with developers merging more than 30 million Dependabot pull requests and GitHub continuing to build tools around smaller, more manageable stacked pull requests.
The bigger story is that AI coding is moving beyond generating snippets. Agents are beginning to participate across the entire development process, from creating changes to reviewing and fixing them.
Developers are not disappearing from that process. Their role is increasingly shifting towards something arguably more important: deciding what the AI should build, determining whether its work is correct and taking responsibility for what ultimately reaches production.






Comments 0