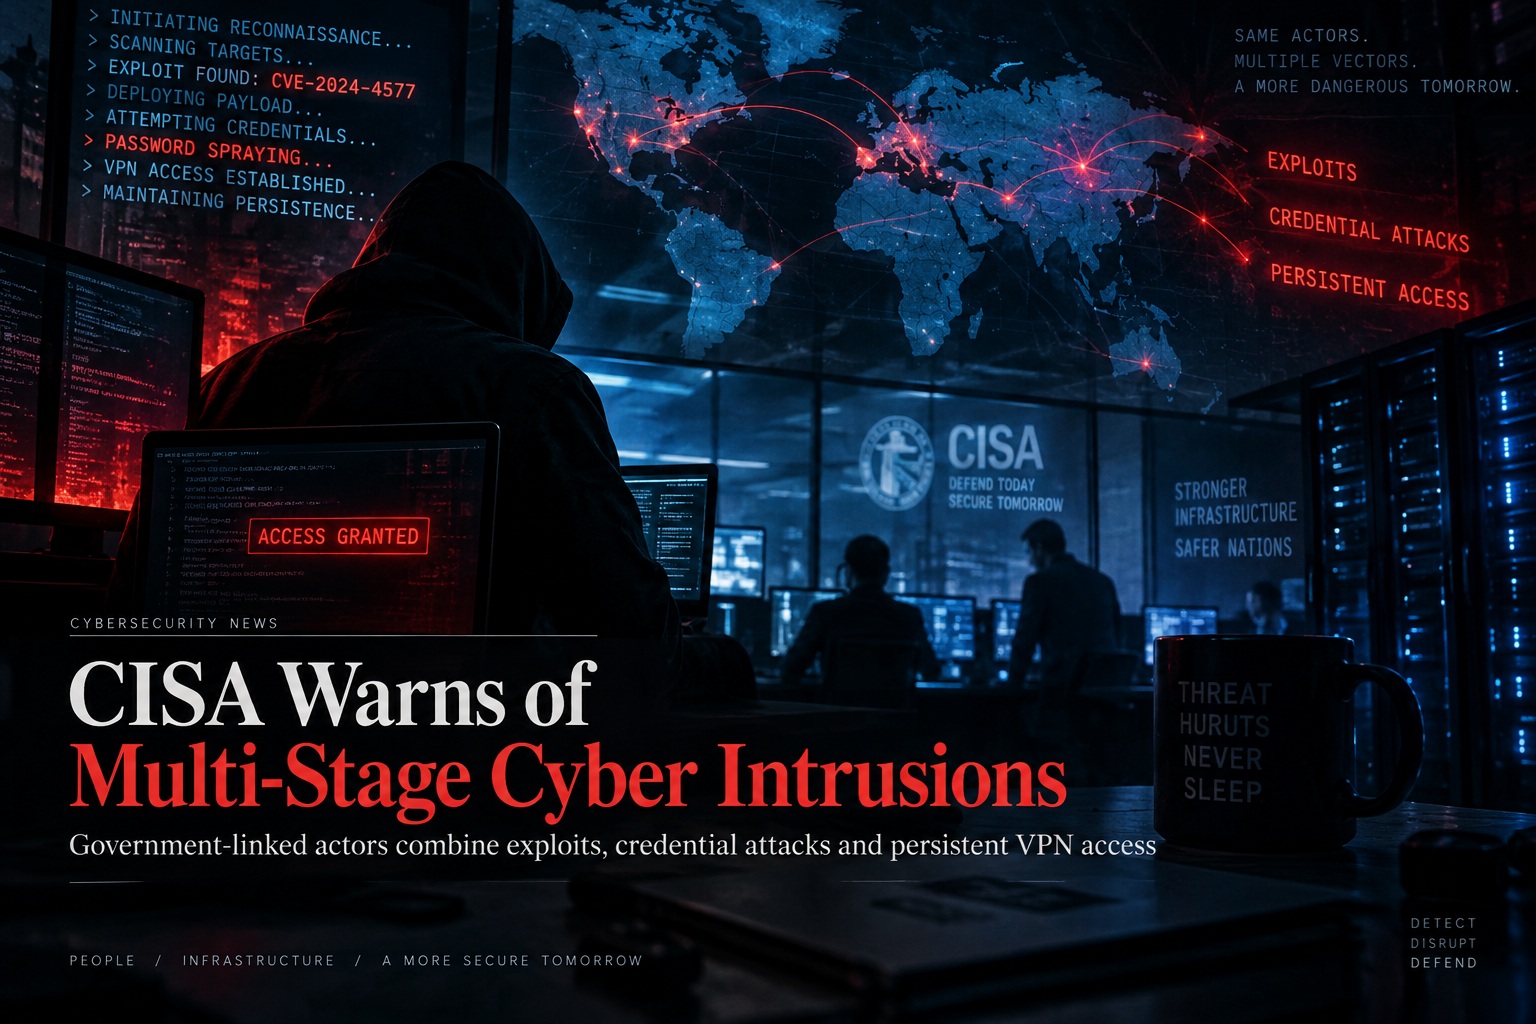
CISA has issued an urgent warning about government-linked cyber threat actors using a combination of automated reconnaissance, known software vulnerabilities, credential attacks and persistent remote-access techniques to compromise organisational networks. Rather than depending on a single sophisticated exploit, the attackers are combining multiple weaknesses across web applications, network services, email accounts and identity infrastructure to gain access and steal sensitive information.
The observed campaigns show how attackers can move systematically through an organisation. They begin by scanning internet-facing systems for weaknesses, exploit vulnerable applications, target user accounts through password spraying and then establish persistent access using unauthorised VPN software. Once inside, they collect credentials, email content and Active Directory information before preparing sensitive data for exfiltration.
Eight Known Vulnerabilities Have Been Exploited
Eight vulnerabilities were identified as being successfully exploited during the observed malicious activity. They affect a broad range of technologies, including GNU Bash, ProFTPD, ISC BIND, Apache Struts, Pulse Connect Secure, GitLab, ONLYOFFICE Document Server and Strapi.
The vulnerabilities include:
Several of these vulnerabilities are classified as Critical, while the remainder carry High severity ratings. More importantly, some of them are more than a decade old, demonstrating how legacy systems can remain dangerous long after patches have become available.
Old Vulnerabilities Remain Valuable To Attackers
One of the most striking vulnerabilities in the campaign is CVE-2014-6278, commonly associated with Shellshock. The flaw affects vulnerable versions of GNU Bash and can allow attackers to inject operating-system commands remotely.
Despite being disclosed in 2014, the vulnerability can still provide attackers with an entry point when organisations continue operating outdated systems. Older vulnerabilities are particularly attractive because exploit code and scanning techniques are often widely available, making them easy to automate.
The lesson is simple: a vulnerability does not become harmless because it is old. If the affected system remains reachable and unpatched, attackers can continue exploiting it years later.
Critical File Access Vulnerabilities Are Also Being Abused
CVE-2015-3306 in ProFTPD and CVE-2019-11510 in Pulse Connect Secure can allow attackers to obtain files that should normally remain protected. These vulnerabilities are particularly serious because configuration files may contain passwords, certificates, API keys or other sensitive information.
An attacker who retrieves these files may be able to use the information to compromise additional systems. What initially appears to be a simple file-reading vulnerability can therefore become the first stage of a much larger intrusion.
This demonstrates why organisations should assess vulnerabilities based on their wider potential impact rather than simply looking at the immediate technical effect.
GitLab And Apache Struts Can Lead To Remote Code Execution
The attackers have also exploited vulnerabilities capable of providing direct code execution. CVE-2021-22205 affects vulnerable GitLab installations and can allow attackers to execute malicious code remotely.
Development platforms such as GitLab can be particularly valuable targets because they may contain source code, deployment configurations, credentials and details about internal infrastructure. Compromising such a system could potentially expose information far beyond the original server.
Apache Struts is also targeted through CVE-2016-3081, another command injection vulnerability that can result in remote code execution across affected versions.
ONLYOFFICE, BIND And Strapi Are Also Part Of The Attack Surface
Other exploited weaknesses include CVE-2021-3199 in ONLYOFFICE Document Server, which can allow unauthorised file writing through path traversal, and CVE-2015-5477 in ISC BIND, which can cause denial of service.
Strapi is affected through CVE-2023-22894, involving insecure handling of sensitive information that may result in information disclosure.
The variety of affected products shows that these attackers are not focusing on a single technology ecosystem. Instead, they are scanning broadly and exploiting whatever vulnerable internet-facing systems they discover.
Automated Reconnaissance Comes First
The attacks begin with large-scale automated reconnaissance. Tools such as Nmap, Masscan, Fscan and WPScan are used to identify exposed services, web applications and systems that may contain exploitable vulnerabilities.
This allows attackers to scan large numbers of targets quickly rather than manually researching each organisation. Once a vulnerable service is discovered, exploitation can either be automated or handed over to an operator for more targeted activity.
For organisations, this means any exposed vulnerable service should be considered discoverable. Security through obscurity is ineffective when automated scanners continuously search the internet for weak systems.
Government-Linked Threat Activity Shows A Structured Approach
The observed tactics are associated with government-linked cyber operations that combine large-scale scanning with more targeted exploitation once a promising victim is identified. The techniques overlap with activity previously associated with several Chinese-linked threat groups.
The important point is not simply which group name is attached to the campaign. The bigger concern is the operational approach: automated discovery finds vulnerable organisations, while experienced operators take over after initial access to pursue credentials, persistence and sensitive information.
This combination provides both scale and flexibility, allowing attackers to target many organisations while still adapting to individual network environments.
Fake Login Prompts Are Used To Steal Credentials
Cross-site scripting attacks have also been used to display fraudulent login prompts. Users who believe they are interacting with a legitimate authentication page may unknowingly submit their usernames and passwords directly to attackers.
Credential theft can sometimes be even more useful than exploiting another vulnerability. Valid login credentials may provide access to email, VPN services, cloud platforms and other enterprise systems while producing traffic that initially resembles legitimate user activity.
This is why identity security has become just as important as traditional vulnerability management.
Microsoft Exchange And Microsoft 365 Face Password Spraying
The threat actors are also conducting password-spraying attacks against Microsoft Exchange and Microsoft 365 environments. Instead of trying many passwords against one account, password spraying typically uses a small number of common passwords across many accounts.
This approach reduces the chance of triggering traditional account-lockout protections while still providing opportunities to compromise weak credentials.
Successful access to email systems can expose internal conversations, confidential attachments, business relationships and password-reset messages. A compromised mailbox can also be used to launch highly convincing phishing attacks against colleagues, customers or suppliers.
SoftEther VPN Is Used For Persistence
After gaining access, attackers have been observed deploying SoftEther VPN software to maintain persistent remote connectivity. Related executables may be renamed using legitimate-looking Windows filenames such as conhost.exe or dllhost.exe to make the activity less obvious.
This is particularly important from an incident-response perspective. Simply patching the original vulnerability may not remove an attacker who has already established another method of access.
Organisations responding to a compromise should therefore investigate persistence mechanisms rather than assuming that patching alone has solved the problem.
Active Directory Becomes A High-Value Target
Once inside the environment, the attackers collect credentials and Active Directory information. One of the techniques observed is DCSync, which can allow an attacker with sufficient privileges to imitate a domain controller and request password-related information.
Active Directory is an extremely valuable target because it sits at the centre of authentication for many enterprise environments. Gaining sufficient control over it can allow attackers to expand from one compromised system to a much larger portion of the organisation.
This makes unusual directory activity, privilege escalation and suspicious domain-controller behaviour especially important to monitor.
Email And Sensitive Information Are Collected
The attackers also collect email content and other sensitive information after establishing access. Automated tools are used to gather messages, stage information locally and transfer the collected data to external infrastructure.
Data may also be encrypted before exfiltration to make malicious outbound transfers more difficult to inspect. The ultimate objective appears to include intelligence collection rather than simply gaining access to systems.
Email environments are particularly useful for espionage because they can reveal internal planning, organisational relationships, commercial decisions and current activities.
Not Every Targeted Technology Requires A Vulnerability
Microsoft Exchange, Microsoft 365, Active Directory and SoftEther VPN also appear throughout the attack chain, but this does not necessarily mean that attackers are exploiting a specific software vulnerability in each product.
A fully patched Microsoft 365 environment can still be compromised if an attacker successfully guesses or steals valid user credentials and multi-factor authentication is not enforced. Likewise, legitimate remote-access software can become malicious when installed or controlled by an attacker.
This highlights why cybersecurity cannot rely entirely on patching. Identity security, configuration management, monitoring and access controls remain equally important.
Organisations Should Patch Vulnerable Systems Immediately
Organisations should identify whether any affected software versions remain within their environments and upgrade them to currently supported, patched versions. Internet-facing systems deserve particular attention because attackers can discover them easily through automated scanning.
Older internal systems should not be ignored either. Once attackers gain an initial foothold, they may be able to reach systems that are not directly exposed to the internet.
Accurate asset inventories are critical. An organisation cannot patch or retire a vulnerable system if nobody knows it is still running.
Close Unnecessary Ports And Services
Services and network ports that are not required for business operations should be disabled or restricted. Every unnecessary internet-facing service increases the organisation's attack surface.
Old management interfaces, forgotten applications and legacy services can remain accessible for years without attracting internal attention. Automated internet scanners, however, may eventually find them.
Reducing unnecessary exposure can eliminate entire attack paths and should be treated as an important defensive measure alongside patch management.
MFA Is Essential Against Password Attacks
Multi-factor authentication should be enforced for security-sensitive accounts and especially for users accessing internet-facing services. Administrator accounts, remote-access accounts and cloud identities should receive the strongest protection.
For Microsoft 365 and Exchange Online environments, organisations can use Microsoft Entra security defaults or implement Conditional Access policies where licensing permits.
MFA significantly reduces the usefulness of stolen or guessed passwords. Even if attackers identify valid credentials, they still need to bypass the additional authentication requirement before gaining access.
The Campaign Covers Almost The Entire Attack Lifecycle
The techniques observed span nearly every major stage of an intrusion. Reconnaissance begins with vulnerability scanning, followed by initial access through vulnerable systems or compromised credentials.
Execution may involve PowerShell, Unix shell, Python or JavaScript. Persistence is established through external remote services, while attackers disguise files and utilities to avoid detection.
Credential access includes password guessing, password spraying and DCSync. The attackers then collect email, archive information, stage data locally and automatically exfiltrate it from the environment.
This demonstrates why effective defence requires visibility across endpoints, networks, identities, cloud platforms and sensitive data rather than relying on a single security product.
Final Thoughts
The latest warning demonstrates how serious cyber espionage campaigns do not necessarily require a new zero-day vulnerability. Government-linked threat actors are successfully combining automated scanning, years-old software weaknesses, credential attacks, persistent VPN access and identity compromise to move through organisational networks.
Perhaps the most important lesson is how many stages defenders have an opportunity to disrupt. Keeping accurate asset inventories, patching internet-facing systems, closing unnecessary services, enforcing MFA and monitoring unusual VPN, email and privileged-account activity can collectively make these campaigns much harder to execute successfully.
The fact that several exploited vulnerabilities have been known for years should be particularly concerning. Sometimes the most dangerous weakness is not a newly discovered flaw, but an old one that an organisation simply forgot to fix.






Comments 0