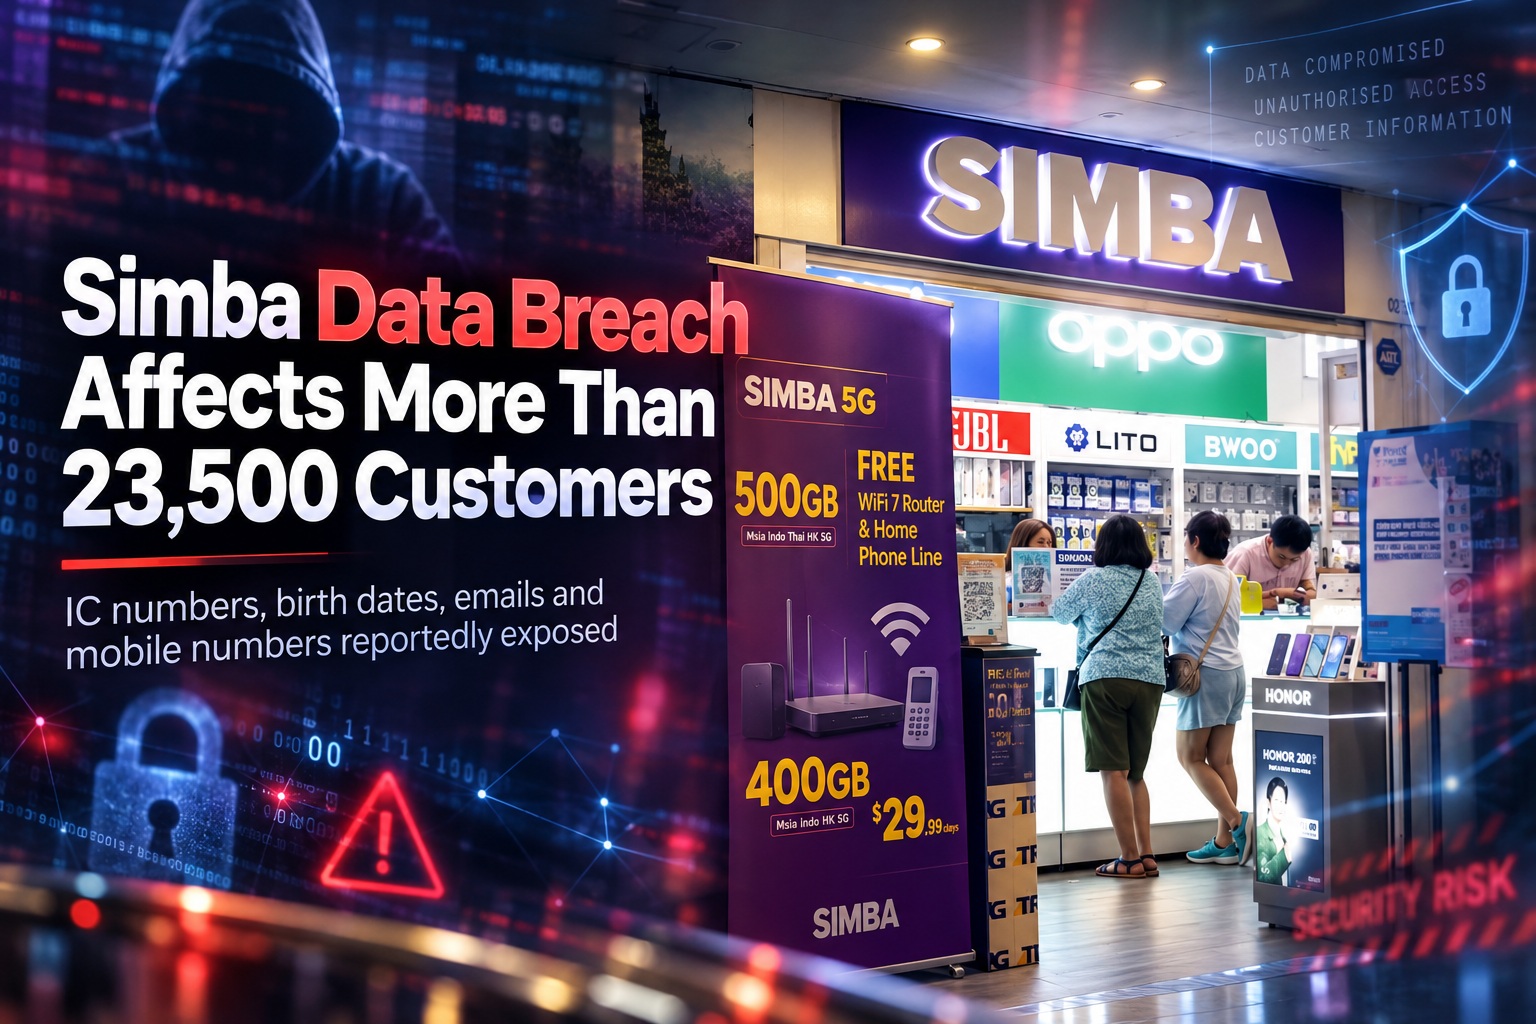
Telecommunications provider Simba has confirmed a data breach affecting 23,549 customers, with personal information including names, identity card numbers and dates of birth exposed during the incident.
Based on the company's investigation so far, the compromised information also included customers' mobile numbers and email addresses. The affected records relate to people who had previously registered for Simba's telecommunications services.
Incident Discovered and Resolved Within a Day
Simba said it discovered the security incident on 24 September and had resolved the issue by the following day. The company did not provide detailed information about how the breach occurred or how the data was accessed, but said it had taken immediate steps to contain the incident.
The telco stressed that credit card and bank account information were not affected, reducing the likelihood of direct financial theft from the breach itself.
Simba also said there was currently no evidence indicating that the exposed personal information had been maliciously used.
Identity Information Still Creates Potential Risk
While financial details were not compromised, the exposed information remains sensitive. Names, identity card numbers, birth dates, email addresses and mobile numbers can potentially be combined in social engineering or impersonation attempts.
Information of this nature can be particularly useful to scammers because it may help make fraudulent calls, phishing emails or account-verification requests appear more convincing.
Affected customers should therefore remain cautious about unexpected messages or calls that reference personal details and should avoid sharing passwords, one-time passwords or additional identity information without independently confirming who they are dealing with.
Simba Reviewing Existing Security Measures
The company said it is treating the incident seriously and has started reviewing its existing security controls around core infrastructure and systems.
Simba is also working with the relevant authorities as part of its response. However, the company has not disclosed whether the breach involved an external intrusion, internal system issue or another type of security incident.
Further information may emerge as the investigation progresses.
Affected Customers Will Be Contacted by Email
Simba has begun notifying customers whose information was involved in the breach. Notifications are being sent progressively through email, with the company expecting the process to be completed within approximately one week.
Customers receiving an official notification should review the details carefully and remain alert for follow-up phishing attempts. Data breaches are sometimes followed by fraudulent messages pretending to come from the affected company, especially once attackers know customers may be expecting security-related communications.
As a precaution, users should access Simba's services directly through known official channels rather than clicking unexpected links contained in emails or text messages.
Singapore's Privacy Regulator Is Investigating
Singapore's Personal Data Protection Commission (PDPC) has confirmed that it is aware of the incident and has started an investigation.
The regulator's involvement is expected given the type of personal information affected and the number of customers involved. The investigation will likely examine how the incident occurred, what safeguards were in place and whether Simba's response met its obligations under Singapore's personal-data protection requirements.
For now, the full technical cause and scope of the breach have not been publicly disclosed.
Final Thoughts
The Simba breach is another reminder that a security incident does not need to expose payment information to create meaningful risk. Identity card numbers, dates of birth, email addresses and phone numbers can still provide valuable material for phishing, impersonation and other forms of social engineering.
The company says the incident has been resolved and that there is currently no evidence of malicious misuse of the affected information. Still, with 23,549 customers impacted, those involved should remain particularly cautious about suspicious calls, messages or emails over the coming weeks.
The PDPC investigation should eventually provide a clearer picture of what happened and whether additional action is required.






Comments 0